How to Know What Security Type WiFi You Need in 2024
WiFi security isn’t just a technical detail—it’s the first line of defense against unauthorized access, data theft, and even home network hijacking. Yet, most users never pause to know what security type WiFi their router is broadcasting, let alone whether it’s the strongest option available. The default settings on most routers often leave networks vulnerable, with outdated protocols like WEP still lurking in some older devices. Understanding the nuances between WPA3, WPA2, and legacy standards isn’t just for IT specialists; it’s a critical skill for anyone who values privacy in an era where smart devices constantly scan for weak signals.
The problem deepens when users assume "strong encryption" means their network is secure. A router displaying "WPA2-PSK" might sound technical, but without verifying its configuration, you could be exposing sensitive data to brute-force attacks. Even worse, some ISPs or pre-configured routers default to knowing what security type WiFi is active—often hiding it behind obscure menu paths. This ambiguity forces users to make uninformed choices, prioritizing convenience over security. The stakes are higher than ever: a single misconfigured network can turn your home into an open relay for cybercriminals targeting everything from banking credentials to IoT devices.

The Complete Overview of WiFi Security Types
WiFi security types define how data is encrypted between your devices and the router, determining who can access your network and whether their communications remain private. The most critical distinction lies between knowing what security type WiFi your router supports and which one you actively enforce. Modern standards like WPA3 offer forward secrecy and protection against offline brute-force attacks, while older protocols like WPA2 (or worse, WEP) rely on outdated cryptographic methods vulnerable to exploits. The choice isn’t just about speed—it’s about balancing performance with resilience against evolving threats like KRACK attacks, which specifically target WPA2’s handshake process.Most routers advertise their security capabilities in the admin panel under "Wireless Settings," but the terminology can be misleading. Terms like "AES" or "TKIP" refer to encryption methods within a security protocol (e.g., WPA2-AES is stronger than WPA2-TKIP). Ignoring these details leaves networks exposed to downgrade attacks, where attackers force devices to use weaker encryption. Even if your router lists "WPA3," verifying its implementation (Personal vs. Enterprise) and whether it supports SAE (Simultaneous Authentication of Equals) is essential—especially for networks handling sensitive transactions or voice communications.
Historical Background and Evolution
The first widely adopted WiFi security standard, WEP (Wired Equivalent Privacy), launched in 1999 with the IEEE 802.11b protocol. Designed to provide basic confidentiality, WEP relied on a static 40-bit or 128-bit key—an approach so flawed that it could be cracked in minutes using freely available tools like Aircrack-ng. By 2003, the WiFi Alliance introduced WPA (WiFi Protected Access) as an interim solution, using TKIP (Temporal Key Integrity Protocol) to dynamically generate keys. While WPA was a massive improvement, its reliance on TKIP—combined with vulnerabilities in the 4-way handshake—proved insufficient against determined attackers.The breakthrough came in 2004 with the ratification of 802.11i, which standardized WPA2 and replaced TKIP with AES (Advanced Encryption Standard), a military-grade algorithm resistant to brute-force attacks. For over a decade, WPA2-AES became the gold standard, adopted by nearly all routers and devices. However, in 2017, the KRACK attack exposed a critical flaw in WPA2’s handshake process, allowing attackers to decrypt traffic even with strong encryption. This led to the development of WPA3, finalized in 2018, which eliminated these vulnerabilities through SAE (a password-authenticated key exchange) and individualized data encryption, ensuring that even if one device is compromised, others remain secure.
Core Mechanisms: How It Works
At its core, knowing what security type WiFi your network uses determines how encryption keys are generated, distributed, and refreshed. WPA2, for example, uses a pre-shared key (PSK) or enterprise credentials to authenticate devices, then derives session keys via the 4-way handshake. Each packet is encrypted with a unique key (via CCMP in AES mode), but the handshake itself becomes a target for KRACK-style attacks. WPA3, by contrast, replaces the handshake with SAE, a password-based exchange that resists offline brute-force attempts. Even if an attacker captures the handshake, they cannot reverse-engineer the password without real-time interaction with the router.The transition from WPA2 to WPA3 also introduced Opportunistic Wireless Encryption (OWE), a fallback mechanism that automatically encrypts connections between WPA3-capable devices, even if the network defaults to WPA2. This ensures backward compatibility while mitigating risks. Meanwhile, the WiFi Certified Easy Connect feature simplifies setup for IoT devices, which often lack traditional interfaces to know what security type WiFi they’re joining. Understanding these mechanics isn’t just academic—it directly impacts whether your network can withstand modern attack vectors like Evil Twin or Rogue Access Point exploits.
Key Benefits and Crucial Impact
Securing your WiFi isn’t about paranoia; it’s about risk mitigation in a landscape where default passwords (like "admin/admin") are still common and IoT devices often lack basic security updates. The right security type can prevent unauthorized users from siphoning bandwidth, intercepting sensitive data, or even using your network for illegal activities—all while protecting your liability. For businesses, the consequences of a breach extend to compliance violations (e.g., GDPR fines for exposed customer data). Even at home, a compromised network can lead to identity theft or ransomware infections on connected devices.Table of Contents
- The Complete Overview of WiFi Security Types
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: How do I check what security type WiFi my router is using?
- Q: Is WPA2 still secure if I can’t upgrade to WPA3?
- Q: What’s the difference between WPA3 Personal and Enterprise?
- Q: Can I use WPA3 if my devices don’t support it?
- Q: Why does my router show "Mixed Mode" for security?
- Q: How often should I update my WiFi security settings?
As cybersecurity expert Bruce Schneier once noted:
"Security isn’t a product; it’s a process. The moment you stop updating your WiFi encryption, you’re already behind."The choice of security type directly influences performance, compatibility, and resilience. A poorly configured WPA2 network might offer faster speeds but at the cost of vulnerability, while WPA3’s stronger encryption adds negligible latency to most consumer devices. The trade-off isn’t just technical—it’s financial. A single data breach can cost small businesses thousands in recovery, not to mention reputational damage.
Major Advantages
- Protection Against Brute-Force Attacks: WPA3’s SAE protocol eliminates the risk of offline password cracking, a major flaw in WPA2.
- Forward Secrecy: Even if a long-term key is compromised, WPA3’s per-session keys prevent retroactive decryption of past traffic.
- Enhanced IoT Security: Features like OWE and Easy Connect reduce the attack surface for resource-constrained devices.
- Regulatory Compliance: Many industries (healthcare, finance) require WPA3 for handling sensitive data under standards like HIPAA or PCI DSS.
- Future-Proofing: WPA3 is designed to adapt to quantum computing threats, unlike WPA2, which may become obsolete.
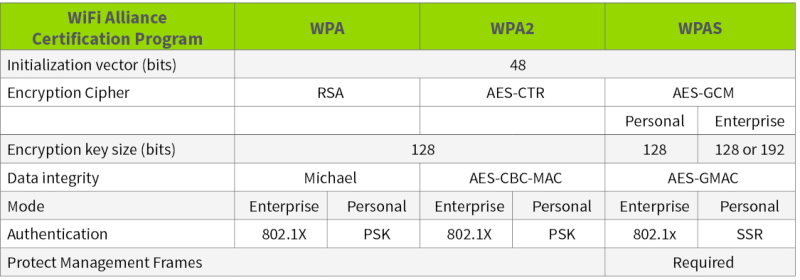
Comparative Analysis
| Security Type | Key Features & Risks |
|---|---|
| WEP | Legacy standard (40/128-bit keys). Vulnerable to cracking in seconds. Never use. |
| WPA (TKIP) | Interim solution for WEP’s flaws. Still vulnerable to chopchop attacks. Avoid unless legacy devices demand it. |
| WPA2 (AES/CCMP) | Industry standard for years. Secure against brute force but susceptible to KRACK if not patched. Requires regular firmware updates. |
| WPA3 (SAE/OWE) | Current gold standard. Resistant to offline attacks, supports individualized encryption, and includes IoT-friendly features. |
Future Trends and Innovations
The next frontier in WiFi security lies in quantum-resistant encryption, as researchers develop post-quantum cryptographic algorithms to counter threats from quantum computers. While WPA3 is designed to be future-proof, the industry is already exploring WiFi 6E and 7 integrations with stronger authentication frameworks. Another emerging trend is AI-driven threat detection, where routers analyze traffic patterns to flag anomalies—such as a sudden influx of devices—before an attack occurs. Meanwhile, passwordless authentication (using biometrics or hardware tokens) is gaining traction in enterprise environments, though consumer adoption remains limited.For home users, the shift toward mesh networks complicates security management, as each node must enforce consistent policies. Vendors are responding with unified dashboards that let users know what security type WiFi is applied across all nodes, but misconfigurations still plague multi-device setups. The key takeaway: static security settings are obsolete. The future demands dynamic, adaptive encryption that evolves with threats—something only achievable through regular updates and proactive monitoring.

Conclusion
Ignoring the question of knowing what security type WiFi your network uses is akin to leaving your front door unlocked while advertising your valuables online. The technical barriers to upgrading are minimal—most modern routers support WPA3 with a firmware update—but inertia and misinformation keep millions exposed. The good news is that the tools to secure your network are within reach: start by auditing your router’s settings, disable WPS (a notorious vulnerability), and enforce WPA3 where possible. For older devices, at least ensure WPA2-AES is enabled and disable TKIP entirely.The digital landscape rewards vigilance. A single misstep—like assuming "WPA2" is sufficient—can turn your network into a liability. By understanding the nuances of each security type, you’re not just protecting data; you’re preserving autonomy in an era where connectivity is inseparable from control.
Comprehensive FAQs
Q: How do I check what security type WiFi my router is using?
To know what security type WiFi your router is broadcasting, log into its admin panel (usually via 192.168.1.1 or similar). Navigate to "Wireless Settings" or "Security Settings." Look for fields labeled "Security Mode," "Encryption Type," or "WiFi Standard." If you’re unsure, use a network analyzer like Wireshark or inSSIDer to scan for active security protocols.
Q: Is WPA2 still secure if I can’t upgrade to WPA3?
WPA2-AES is still secure if properly configured—meaning you’ve disabled TKIP, enabled CCMP, and applied strong passwords. However, it’s vulnerable to KRACK attacks if your router’s firmware isn’t updated. For maximum security, prioritize WPA3. If stuck with WPA2, at least ensure it’s not mixed with WEP or TKIP.
Q: What’s the difference between WPA3 Personal and Enterprise?
WPA3 Personal uses a pre-shared key (PSK) like WPA2, but with SAE for stronger password protection. WPA3 Enterprise replaces PSKs with 802.1X authentication (e.g., certificates or RADIUS), ideal for businesses. The key difference is scalability: Enterprise supports centralized management, while Personal is simpler for home users.
Q: Can I use WPA3 if my devices don’t support it?
Yes, via OWE (Opportunistic Wireless Encryption). WPA3 routers can downgrade to WPA2 for older devices while still encrypting traffic between WPA3-capable devices. This ensures backward compatibility without sacrificing security for modern devices.
Q: Why does my router show "Mixed Mode" for security?
"Mixed Mode" means your router supports multiple security types (e.g., WPA3 and WPA2) to accommodate older devices. While convenient, it weakens security by allowing connections to use weaker protocols. Disable Mixed Mode if all your devices support WPA3, or at least prioritize WPA3-AES over WPA2-TKIP.
Q: How often should I update my WiFi security settings?
Check for router firmware updates every 3–6 months, as manufacturers frequently patch vulnerabilities. If you notice slower speeds or unusual activity, audit your security type immediately. Proactively know what security type WiFi you’re using ensures you’re not caught off guard by new exploits.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Filmfestivalcircuit.