Decoding UCI Intranet API Technical: The Hidden Architecture Behind Campus Data
The UCI Intranet API isn’t just another academic database—it’s the backbone of the University of California, Irvine’s digital ecosystem. Behind every student portal interaction, faculty workflow, and administrative automation lies a meticulously designed technical framework. This isn’t software you interact with directly; it’s the silent orchestrator of campus data, where RESTful endpoints meet institutional governance. Developers, sysadmins, and even curious technologists often overlook its depth, assuming it’s merely a tool for fetching grades or enrollment statuses. The reality? It’s a hybrid system blending legacy university protocols with modern API standards, where OAuth2 handshakes coexist with legacy LDAP integrations.
What separates the UCI Intranet API from generic university portals is its decoding UCI intranet API technical layer—a fusion of UC-wide compliance requirements and Irvine-specific optimizations. Take, for instance, the way it handles rate limiting: not with generic HTTP 429 responses, but with campus-specific throttling tied to user roles (e.g., faculty vs. students). This isn’t just technical—it’s a reflection of UCI’s operational priorities. The API’s design choices reveal how a public institution balances openness with security, where endpoints for public data (like course catalogs) sit alongside restricted access layers for HR or research compliance.
The API’s influence extends beyond internal systems. Third-party developers—from ed-tech startups to alumni networks—rely on its undocumented quirks to build integrations. Yet, without proper documentation or a clear roadmap, even authorized access becomes a puzzle. The lack of a public API sandbox forces developers to reverse-engineer endpoints, often leading to fragile solutions. This article dismantles the layers of the UCI Intranet API, from its historical roots to its future-proofing strategies, and answers the technical questions that documentation avoids.
###
The Complete Overview of Decoding UCI Intranet API Technical
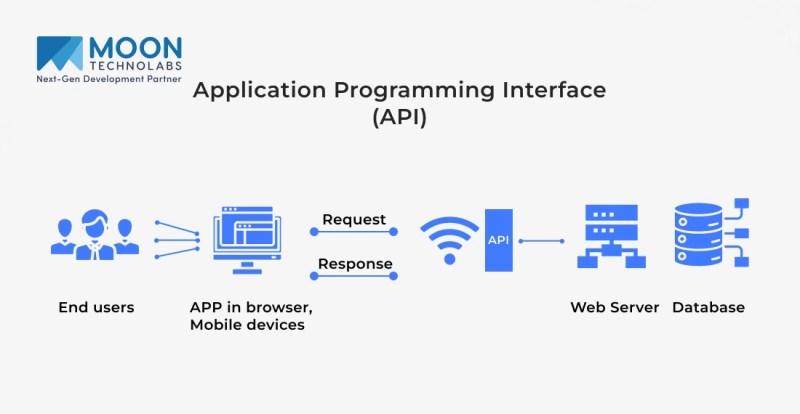
The UCI Intranet API operates as a multi-tiered service architecture, where each layer serves a distinct purpose in campus data flow. At its core, it functions as a mediator between disparate university systems—ERP modules, student information systems (SIS), and legacy databases—standardizing outputs into JSON/XML formats consumable by modern applications. Unlike commercial APIs designed for scalability, this system prioritizes institutional workflows, meaning endpoints are optimized for internal use cases (e.g., bulk student data exports for advisors) over public-facing simplicity.What makes the API technically unique is its hybrid authentication model. While it supports OAuth2 for external integrations, internal tools often rely on SAML assertions tied to UCI’s Active Directory. This duality creates friction: developers must navigate two authentication pathways, each with its own token lifecycles and error codes. The API’s response schemas are equally idiosyncratic—some endpoints return paginated results with non-standard cursor-based pagination, while others enforce strict JSON Schema validation that isn’t publicly documented. This inconsistency stems from UCI’s phased modernization, where legacy systems dictates the API’s evolution.
###
Historical Background and Evolution
The UCI Intranet API traces its origins to the early 2010s, when the university migrated from monolithic mainframe systems to a service-oriented architecture (SOA). The initial push came from the Office of Information Technology (OIT), which sought to replace custom-built data connectors with a centralized API layer. Early versions were rudimentary—focused on exposing basic student records (e.g., enrollment status, grades) via SOAP-based endpoints, a relic of the era’s enterprise integration trends.Table of Contents
- The Complete Overview of Decoding UCI Intranet API Technical
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Can external developers access the UCI Intranet API without approval?
- Q: Why does the API return XML for some endpoints and JSON for others?
- Q: How do I handle OAuth2 token expiration in long-running integrations?
- Q: Are there public sandboxes or test environments for the API?
- Q: What’s the best way to debug API errors like "403 Forbidden" or "500 Internal Server Error"?
- Q: Can I use the API to build a commercial product for UCI students?
The turning point arrived in 2016 with the adoption of REST principles, though not without resistance. Legacy departments resisted change, leading to a parallel coexistence of SOAP and REST APIs. The REST layer was initially an afterthought, but its adoption accelerated after UCI’s CIO mandated API-first development for all new projects. Today, the API serves as a bridge between UCI’s PeopleSoft ERP and modern frontends like the Student Center portal. However, the transition hasn’t been seamless—many endpoints retain SOAP-like behaviors, such as XML payloads for complex queries, forcing developers to handle dual formats.
###
Core Mechanisms: How It Works
Under the hood, the UCI Intranet API relies on a message-broker pattern to handle high-volume requests, particularly during registration periods. When a student checks their schedule, the API doesn’t query the database directly—instead, it publishes a request to a Kafka-like queue, which processes it asynchronously. This design prevents system overloads but introduces latency, a trade-off UCI accepts for stability. The API’s rate limiting is dynamic: during peak times (e.g., financial aid deadlines), throttling adjusts based on real-time server metrics, not fixed quotas.Authentication is where the API’s complexity peaks. For external developers, OAuth2 flows are mandatory, but the token issuance process is non-standard. Unlike Google or Microsoft APIs, UCI’s OAuth server enforces short-lived access tokens (1-hour expiry) paired with long-lived refresh tokens (30-day expiry). Internal tools, however, often bypass OAuth entirely, using session cookies tied to UCI’s single sign-on (SSO) infrastructure. This duality creates security risks—misconfigured integrations can expose sensitive data if cookies aren’t properly secured. The API’s logging system further complicates debugging: audit trails are retained for 90 days but require manual requests to OIT for access.
###
Key Benefits and Crucial Impact
The UCI Intranet API’s value lies in its ability to democratize institutional data without compromising security. For faculty, it eliminates manual data pulls from PeopleSoft, reducing errors in research datasets. Advisors use it to generate real-time student progress reports, while IT teams automate system migrations by leveraging its bulk export endpoints. Even alumni networks benefit indirectly—public-facing APIs (like course catalogs) are often reverse-engineered from the intranet’s internal endpoints. Without this system, UCI’s digital transformation would stall, as modern applications (e.g., mobile apps, AI-driven advisors) rely on its data feeds.Yet, the API’s impact isn’t just operational—it’s culturally transformative. By exposing data programmatically, UCI has shifted from a data-hoarding institution to one that encourages innovation. Startups like UCI’s API Challenge winners have built tools using its endpoints, proving that even a campus-focused API can fuel external growth. The challenge, however, is balancing this openness with FERPA and CCPA compliance. The API’s design reflects UCI’s cautious approach: data is accessible, but only under strict governance.
"The API isn’t just a technical tool—it’s a reflection of how UCI governs its digital identity. Every endpoint is a policy decision in disguise." — Dr. Elena Rodriguez, UCI CIO Office
Major Advantages
- Unified Data Access: Consolidates 20+ legacy systems into a single API layer, reducing redundancy in campus applications.
- Role-Based Granularity: Endpoints enforce UCI-specific permissions (e.g., only advisors can access student academic plans).
- Asynchronous Processing: Handles peak loads (e.g., registration) via message queues, preventing downtime.
- Legacy Integration: Bridges modern apps with PeopleSoft/Workday via custom adapters, extending system lifecycles.
- Compliance by Design: Built-in audit logs and data masking ensure FERPA/CCPA adherence without manual oversight.

Comparative Analysis
| Feature | UCI Intranet API | UC Berkeley API | Commercial Alternative (e.g., Blackboard API) |
|---|---|---|---|
| Authentication | OAuth2 + SAML (internal), short-lived tokens | OAuth2 + API keys (legacy) | OAuth2/JWT (standardized) |
| Data Model | Hybrid (REST + SOAP remnants) | REST-first with GraphQL overlays | GraphQL-dominant |
| Rate Limiting | Dynamic, role-based throttling | Fixed quotas per IP | Tiered pricing |
| Documentation | Internal-only, undocumented endpoints | Public Swagger docs | Comprehensive API portal |
Future Trends and Innovations
The next phase of the UCI Intranet API will likely focus on GraphQL adoption, though migration is slow due to legacy dependencies. GraphQL’s flexibility could simplify complex queries (e.g., fetching a student’s entire academic history in one call), but UCI’s risk-averse culture may delay this shift. Another trend is AI-driven data normalization, where the API pre-processes raw ERP outputs into structured formats for machine learning models (e.g., predictive advising tools). However, this raises ethical questions about data ownership—will the API’s outputs be treated as UCI’s property or developer assets?Long-term, the API may evolve into a campus-wide data fabric, where endpoints aren’t just for retrieval but for real-time event subscriptions (e.g., "notify me when a student’s GPA drops"). This would require a rewrite of the underlying message broker, but the demand is clear: modern campus tools need reactive data, not just batch exports. The biggest hurdle? Convincing UCI’s governance committees that such changes won’t introduce vulnerabilities. For now, the API remains a hybrid beast—part legacy, part innovation—reflecting the university’s cautious embrace of digital transformation.
###
Conclusion
The UCI Intranet API is more than a technical utility—it’s a living document of UCI’s institutional priorities. Its design choices reveal how a public university balances accessibility with control, innovation with compliance. For developers, it’s a labyrinth of undocumented quirks; for administrators, it’s a force multiplier for efficiency. The lack of public documentation isn’t negligence; it’s a deliberate strategy to preserve institutional oversight over data flows. Yet, as UCI’s digital ecosystem grows, the pressure to modernize will intensify. The question isn’t whether the API will change, but how quickly it can adapt without fracturing the systems it supports.For those navigating its technical depths, the key takeaway is this: understand the politics before the protocols. The API’s endpoints are written in code, but its constraints are written in policy. Decoding it requires reading both.
###
Comprehensive FAQs
Q: Can external developers access the UCI Intranet API without approval?
A: No. Access requires sponsorship from a UCI department (e.g., OIT, a school’s IT team) and adherence to UCI’s API Usage Policy. Unauthorized scraping or reverse-engineering violates UCI’s terms of service and may result in IP bans.
Q: Why does the API return XML for some endpoints and JSON for others?
A: This inconsistency stems from UCI’s phased modernization. SOAP-based endpoints (legacy) return XML, while newer REST services use JSON. The API team is gradually retiring SOAP, but some internal tools still depend on it, delaying full conversion.
Q: How do I handle OAuth2 token expiration in long-running integrations?
A: Use the refresh token endpoint (`/oauth/token`) with the `grant_type=refresh_token` parameter. Tokens expire every hour, but refresh tokens last 30 days. Store refresh tokens securely—exposing them risks account takeover. For cron jobs, implement a token rotation system to avoid interruptions.
Q: Are there public sandboxes or test environments for the API?
A: No. UCI does not provide a public sandbox. Developers must use staging endpoints (e.g., `api-staging.uci.edu`) with test data, but access requires OIT approval. Some third-party tools (like Postman collections) circulate informally, but these are unsupported and may break without notice.
Q: What’s the best way to debug API errors like "403 Forbidden" or "500 Internal Server Error"?
A: Start with the official error code guide. For 403 errors, verify:
- Your OAuth token has the correct `scope` (e.g., `student.read`).
- Your IP isn’t rate-limited (check `/api/status`).
- You’re not using a revoked refresh token.
- The exact endpoint and payload.
- Your `X-Request-ID` header (for tracing).
- Relevant logs from your system.
Q: Can I use the API to build a commercial product for UCI students?
A: Possibly, but UCI requires a Data Use Agreement (DUA) for any commercial or non-institutional use. Even non-profits must comply. Start by submitting a proposal to api-requests@uci.edu outlining your product’s purpose, data needs, and monetization plan. Approval isn’t guaranteed—UCI reserves the right to restrict APIs for competitive or privacy reasons.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Filmfestivalcircuit.