The Definitive Log Complete Guide Managing Your Digital & Physical Systems
Logging isn’t just about recording data—it’s the backbone of operational clarity, accountability, and continuous improvement. Without a structured approach to logging, systems—whether digital, physical, or hybrid—become chaotic, prone to errors, and impossible to audit. The right log complete guide managing your workflows, assets, or personal tasks transforms noise into actionable intelligence, ensuring nothing slips through the cracks.
Yet most professionals and organizations treat logging as an afterthought, implementing it only when problems arise. This reactive approach leads to fragmented records, missed deadlines, and costly inefficiencies. The truth? A well-designed logging system isn’t just a tool—it’s a strategic asset that enhances decision-making, streamlines operations, and future-proofs your processes against disruptions.
Whether you’re overseeing a corporate IT infrastructure, tracking inventory in a warehouse, or managing a personal knowledge base, the principles of effective logging remain constant. The difference between a log complete guide managing your systems and a disorganized mess lies in precision, scalability, and adaptability. This guide cuts through the ambiguity, offering a framework to implement logging that works for any context.
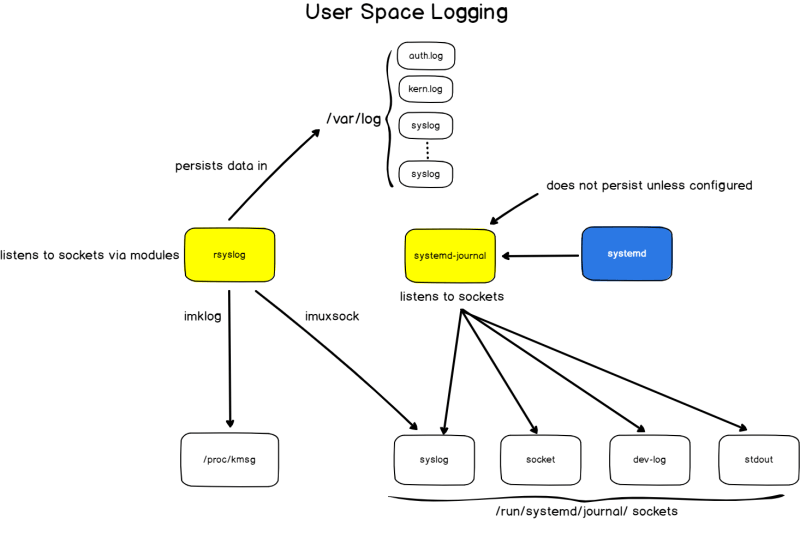
The Complete Overview of Log Management Systems
A log complete guide managing your operations begins with understanding that logging is more than archiving—it’s a dynamic process of capturing, analyzing, and acting on data. At its core, logging serves three primary functions: verification (proving actions were taken), diagnosis (identifying root causes of failures), and compliance (meeting regulatory or internal standards). Without these, even the most sophisticated systems risk becoming black boxes where problems fester unseen.
The evolution of logging has mirrored technological advancements. Early systems relied on manual pen-and-paper records, which were error-prone and difficult to retrieve. The digital revolution introduced structured log files in software, but these were often siloed, making cross-system analysis nearly impossible. Today, modern log management platforms integrate AI-driven parsing, real-time alerts, and centralized dashboards—yet many organizations still operate with outdated practices, missing the full potential of a log complete guide managing your entire ecosystem.
Historical Background and Evolution
The origins of logging trace back to ancient accounting practices, where merchants recorded transactions to prevent fraud and track inventory. By the Industrial Revolution, factories adopted logbooks to monitor machinery performance, a precursor to modern predictive maintenance. The 1970s saw the rise of computer logs in mainframe systems, but these were primarily for debugging, not strategic use. It wasn’t until the 1990s, with the proliferation of networked systems, that logging became a critical component of IT infrastructure—though even then, it was often treated as a secondary function.
Table of Contents
- The Complete Overview of Log Management Systems
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: How do I determine what to log in my system?
- Q: Can I use free tools for log management, or do I need enterprise solutions?
- Q: How do I ensure my logs are secure and compliant?
- Q: What’s the difference between logs and metrics?
- Q: How can I reduce log volume without losing critical data?
The 21st century transformed logging into a discipline. Cloud computing and big data analytics enabled real-time log aggregation, while compliance mandates (e.g., GDPR, HIPAA) forced organizations to adopt structured logging frameworks. Today, a log complete guide managing your systems must account for hybrid environments—where on-premise logs, IoT sensors, and third-party APIs all feed into a unified view. The shift from reactive troubleshooting to proactive optimization defines the modern approach.
Core Mechanisms: How It Works
At its foundation, logging operates on three layers: collection, storage, and utilization. Collection involves capturing events from applications, servers, or devices in a standardized format (e.g., JSON, syslog). Storage requires scalable solutions—whether centralized log servers or cloud-based repositories—to handle volume and retention policies. Utilization turns raw logs into insights through parsing, correlation, and visualization tools, often powered by machine learning to detect anomalies.
The challenge lies in balancing granularity with noise. Over-logging clutters systems with irrelevant data, while under-logging leaves critical gaps. A log complete guide managing your operations must define what to log (e.g., errors, user actions, system metrics), when (real-time vs. batch), and how (structured vs. unstructured). The best systems automate log enrichment—adding context like timestamps, user IDs, or geolocation—to make analysis seamless. Without this precision, logs become a liability rather than an asset.
Key Benefits and Crucial Impact
Organizations that implement a robust log complete guide managing their systems gain a competitive edge. The most immediate benefit is operational resilience: logs serve as a forensic record during outages, allowing teams to pinpoint failures within minutes rather than hours. Beyond crisis management, logging enables predictive analytics, where patterns in system behavior forecast potential failures before they occur. For businesses, this translates to reduced downtime and lower costs—critical in industries where seconds of latency can mean millions in losses.
Yet the impact extends beyond technical efficiency. A well-managed log system enhances accountability by providing an auditable trail of actions, which is non-negotiable in regulated sectors like finance or healthcare. It also improves user experience by identifying friction points in digital workflows. For individuals, a log complete guide managing your personal tasks or health metrics can reveal habits and inefficiencies that manual tracking misses. The return on investment isn’t just financial—it’s strategic.
"Logging is the difference between flying blind and having a control tower. The organizations that treat it as an afterthought will always be reactive; those that build it into their DNA will dominate."
— Dr. Elena Vasquez, Chief Data Officer at LogiQ Analytics
Major Advantages
- Fault Isolation: Logs pinpoint exact causes of system failures, reducing mean time to resolution (MTTR) by up to 70%.
- Compliance Readiness: Structured logs simplify audits for regulations like PCI-DSS or SOX, avoiding costly non-compliance penalties.
- Performance Optimization: By analyzing log patterns, teams can optimize resource allocation (e.g., scaling databases during peak loads).
- Security Hardening: Anomaly detection in logs flags suspicious activity (e.g., brute-force attacks) before damage occurs.
- Knowledge Preservation: Logs act as institutional memory, ensuring critical processes survive employee turnover.
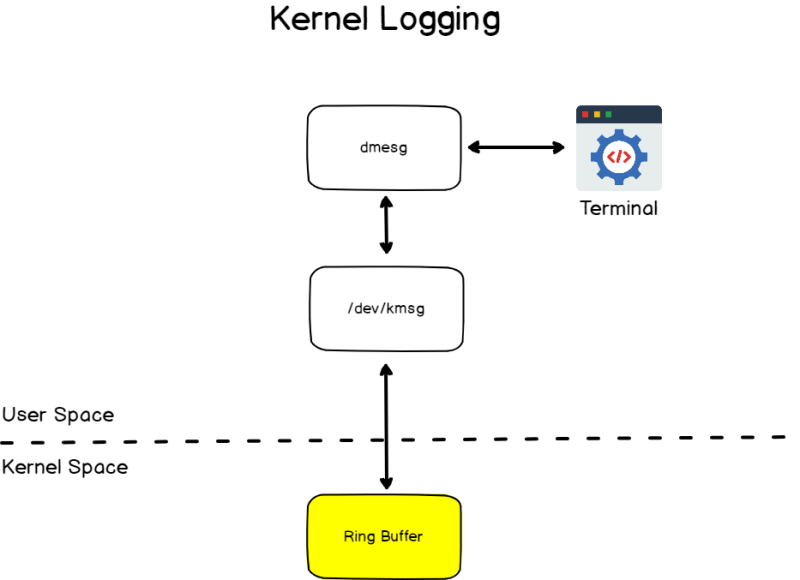
Comparative Analysis
| Traditional Logging | Modern Log Management Platforms |
|---|---|
| Manual or script-based collection; siloed storage. | Automated, real-time ingestion with centralized storage (e.g., ELK Stack, Splunk). |
| Limited to error logs; no contextual enrichment. | Supports structured/unstructured data with metadata (e.g., user IDs, geolocation). |
| Analysis requires manual parsing; slow response to incidents. | AI-driven correlation and alerting (e.g., detecting cascading failures in seconds). |
| Scalability issues with growing data volumes. | Cloud-native architectures with auto-scaling and retention policies. |
Future Trends and Innovations
The next frontier in log management lies at the intersection of AI and edge computing. Current systems rely on centralized log processing, which introduces latency in distributed environments. Future platforms will use edge logging, where devices (e.g., IoT sensors) pre-process and filter logs locally before sending only critical data to the cloud. This reduces bandwidth usage and enables sub-second response times for time-sensitive applications like autonomous vehicles or industrial automation.
Another disruption will come from predictive logging, where machine learning models don’t just analyze past logs but simulate future scenarios. For example, a log complete guide managing your supply chain could predict equipment failures by analyzing historical logs and external factors (e.g., temperature fluctuations). Combined with blockchain-based logging for tamper-proof records, these innovations will redefine trust and transparency in data-driven industries. The key challenge? Ensuring these systems remain interpretable by humans, not just machines.

Conclusion
A log complete guide managing your systems isn’t a one-size-fits-all manual—it’s a living framework that adapts to your specific needs. The organizations that succeed will be those that treat logging as a strategic investment, not a technical obligation. This means integrating logging into every phase of system design, from architecture to user experience, and continuously refining it based on real-world data.
For individuals, the principles are equally applicable: whether tracking fitness metrics, project milestones, or financial transactions, a disciplined approach to logging turns chaos into clarity. The tools may evolve—from paper logs to AI-driven analytics—but the core principle remains unchanged: what you measure, you can manage. Start small, automate where possible, and let your logs become the silent guardian of your success.
Comprehensive FAQs
Q: How do I determine what to log in my system?
A: Prioritize logging critical events (errors, security breaches, user actions) and business metrics (e.g., API response times). Use the 80/20 rule: log the 20% of events that drive 80% of insights. Avoid over-logging by excluding debug-level data unless debugging is a frequent need. Tools like OpenTelemetry help standardize what to collect.
Q: Can I use free tools for log management, or do I need enterprise solutions?
A: Free tools (e.g., Graylog, Fluentd) work for small-scale or low-complexity environments. However, enterprise solutions (e.g., Splunk, Datadog) offer scalability, advanced analytics, and compliance features. For hybrid setups, consider open-source core tools with paid plugins for specific needs.
Q: How do I ensure my logs are secure and compliant?
A: Implement role-based access control (RBAC) to restrict log viewing, encrypt logs in transit and at rest, and enforce retention policies (e.g., 90 days for debug logs, 7 years for audit logs). Use hashing for sensitive data (e.g., PII) and validate against frameworks like NIST SP 800-92 for security best practices.
Q: What’s the difference between logs and metrics?
A: Logs are narrative records of events (e.g., "User X failed to log in at 3:15 PM"), while metrics are quantitative measurements (e.g., "Login failure rate: 5%"). Logs provide context; metrics enable trend analysis. A log complete guide managing your systems should integrate both—for example, using metrics to identify spikes in login failures, then drilling into logs to diagnose the cause.
Q: How can I reduce log volume without losing critical data?
A: Apply log sampling (e.g., log only 1% of debug messages), log filtering (exclude known benign events), and log aggregation (combine multiple logs into a single entry where possible). Tools like Logstash automate filtering, and SIEM systems (e.g., IBM QRadar) help prioritize alerts. Always retain raw logs for compliance, but archive older data in compressed formats.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Filmfestivalcircuit.