How to Spot Chase Phishing Email Scams Before They Steal Your Money
Chase phishing emails arrive daily in inboxes across the country, disguised as urgent security alerts or account updates. These messages use psychological pressure and technical deception to trick recipients into revealing login credentials or transferring funds. The scammers behind them refine their tactics constantly, exploiting human behavior as much as technical vulnerabilities. A single misstep—clicking a malicious link or replying with personal details—can lead to drained accounts, identity theft, or long-term financial damage.
The problem isn’t just the volume of these scams; it’s their evolving sophistication. Cybercriminals now mimic Chase’s branding with near-perfect accuracy, using spoofed email addresses, cloned login pages, and even AI-generated voice calls to create a false sense of legitimacy. What once required obvious grammatical errors now relies on subtle cues—like a slightly off URL or an unexpected request for sensitive information. The stakes are higher than ever, but so are the tools available to detect Chase phishing email scams before they succeed.
Most victims don’t realize they’ve been targeted until it’s too late. The average delay between a phishing attack and discovery is 203 days, according to the FBI’s Internet Crime Complaint Center. By then, the damage—whether through unauthorized transactions, data breaches, or stolen identities—can be irreversible. The key to protection lies in understanding the Chase phishing email spot scams patterns, recognizing the warning signs, and adopting proactive habits that make accounts resilient to fraud.

The Complete Overview of Chase Phishing Email Scams
Chase phishing email scams operate at the intersection of social engineering and technical exploitation. They prey on the natural human tendency to trust authority—especially when that authority appears to be a major financial institution like Chase. The scams typically follow a script: create urgency, impersonate a trusted source, and direct the victim to take an action that compromises security. Whether it’s a "suspicious login" alert, a "pending transaction" notification, or a "security update" request, the goal is the same: to bypass authentication barriers and gain access to sensitive data.
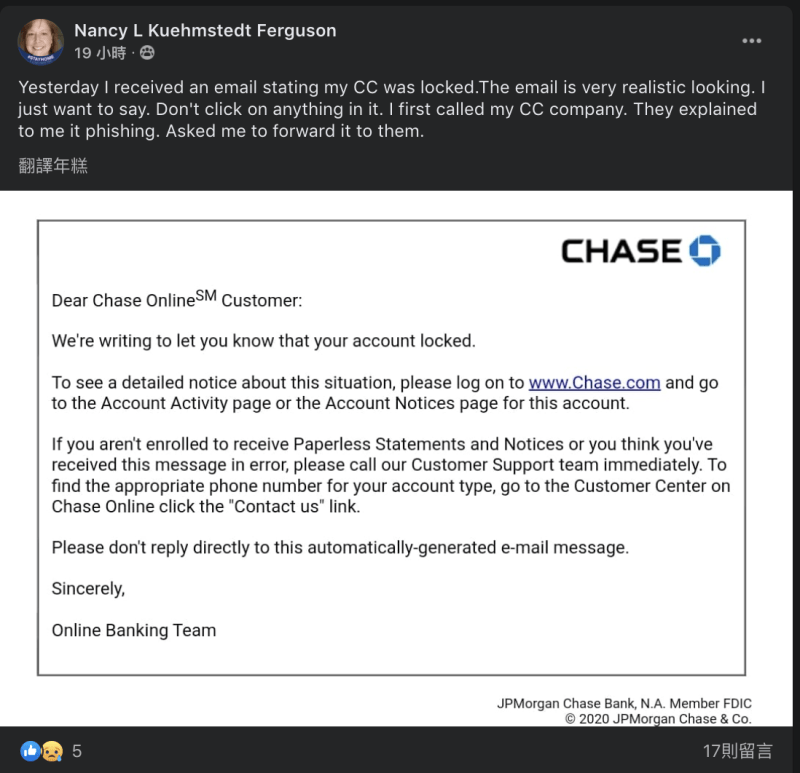
The most effective Chase phishing email scams combine psychological manipulation with technical precision. For example, a scammer might send an email claiming your account has been locked due to "unusual activity" and instruct you to click a link to verify your identity. The link leads to a fake Chase login page that harvests credentials. Alternatively, scammers may use a technique called "spoofing," where the email appears to come from a Chase domain (e.g., security@chase.com) but is actually sent from a malicious server. The result is a seamless deception that even cautious users can fall for without careful scrutiny.
Historical Background and Evolution
The roots of phishing trace back to the mid-1990s, when hackers targeted AOL users with fake password reset requests. By the early 2000s, the term "phishing" was coined, and banks became prime targets as online transactions grew. Chase, as one of the largest U.S. banks, has been a frequent victim of these attacks. Early phishing attempts were crude—poorly written emails with broken English and obvious fake URLs. However, as security awareness improved, so did the sophistication of the scams. Today, Chase phishing email spot scams often use AI to craft personalized messages, deepfake audio for voice phishing (vishing), and even smishing (SMS phishing) to bypass email filters entirely.
Table of Contents
- The Complete Overview of Chase Phishing Email Scams
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: What are the most common red flags in a Chase phishing email?
- Q: Can Chase ever ask for my password or PIN via email?
- Q: What should I do if I’ve already clicked a suspicious link in a Chase phishing email?
- Q: How can I verify if an email is truly from Chase?
- Q: Are there tools or apps that can help detect Chase phishing scams?
- Q: What’s the best way to report a Chase phishing email scam?
The evolution of these scams mirrors broader trends in cybercrime. Where once scammers relied on mass emails to cast a wide net, modern tactics focus on targeted, high-value victims. For instance, a scammer might research a Chase customer’s recent transactions, then send a tailored email claiming a "fraudulent charge" on a specific merchant—using real details to increase credibility. This shift from broad to targeted attacks has made detection more challenging, as the messages now feel eerily relevant to the recipient. Additionally, the rise of open banking APIs has created new attack vectors, allowing scammers to intercept legitimate transaction requests and redirect funds without the victim’s knowledge.
Core Mechanisms: How It Works
The anatomy of a Chase phishing email scam typically follows a three-stage process: deception, exploitation, and extraction. The deception phase begins with the email itself, designed to mimic Chase’s official communications. Scammers use stolen templates, cloned logos, and even legitimate Chase language to create a facade of authenticity. The exploitation phase occurs when the victim interacts with the email—clicking a link, downloading an attachment, or replying with sensitive information. This interaction triggers the scammer’s payload, whether it’s malware, a credential-stealing form, or a wire transfer request. Finally, the extraction phase involves the scammer using the stolen data to drain accounts, open new lines of credit, or sell personal information on the dark web.
One of the most insidious techniques is the use of "homograph attacks," where scammers register domain names that look identical to Chase’s but use different character sets (e.g., replacing "a" with the Cyrillic "а"). For example, a fake Chase login page might use the URL chase-secure-login.com, which appears legitimate at first glance but is actually a malicious site. Another tactic is "session hijacking," where scammers intercept a legitimate Chase session cookie after a victim logs in, allowing them to bypass two-factor authentication (2FA) and access the account directly. Understanding these mechanics is critical to spotting Chase phishing email scams before they compromise security.
Key Benefits and Crucial Impact
Recognizing and avoiding Chase phishing email scams isn’t just about protecting your money—it’s about safeguarding your financial identity and peace of mind. The immediate benefit is financial security: preventing unauthorized transactions, fraudulent charges, and the costly process of recovering stolen funds. Beyond the monetary impact, falling victim to a phishing scam can lead to long-term credit damage, legal complications, and emotional stress. The psychological toll of financial fraud often lingers long after the money is recovered, making prevention a critical aspect of overall well-being.
For businesses and high-net-worth individuals, the stakes are even higher. A single successful phishing attack can expose entire organizations to data breaches, regulatory fines, or reputational harm. Even for individual customers, the ripple effects can be severe—such as being locked out of accounts, dealing with credit bureau disputes, or facing legal liabilities if fraudulent transactions are tied to stolen identities. The proactive approach of learning to spot Chase phishing email scams reduces these risks significantly, making it a cornerstone of modern financial hygiene.
"Phishing is the leading cause of data breaches, and the average cost of a single breach is $4.45 million. Yet, 90% of successful cyberattacks begin with a phishing email." — Verizon 2023 Data Breach Investigations Report
Major Advantages
- Financial Protection: Prevents unauthorized access to accounts, fraudulent transactions, and long-term credit damage.
- Identity Security: Reduces the risk of identity theft, which can take years to resolve and may require legal intervention.
- Operational Efficiency: Avoids the time-consuming process of reporting fraud, disputing charges, and recovering lost funds.
- Regulatory Compliance: Helps individuals and businesses adhere to financial regulations by maintaining secure account practices.
- Psychological Relief: Eliminates the stress and anxiety associated with financial fraud, allowing for greater confidence in digital transactions.

Comparative Analysis
| Aspect | Chase Phishing Email Scams | Traditional Phishing Scams |
|---|---|---|
| Targeting Method | Highly personalized, using real account details and transaction history. | Mass emails with generic content, often sent to thousands of recipients. |
| Technical Sophistication | Uses AI, homograph domains, and cloned login pages for near-perfect deception. | Relies on obvious fake URLs, poor grammar, and generic branding. |
| Response Time | Scammers act quickly—often within hours—to exploit stolen credentials. | Slower response due to lack of tailored information, reducing immediate impact. |
| Detection Difficulty | Harder to spot due to personalized content and professional design. | Easier to identify with clear red flags like broken English or suspicious links. |
Future Trends and Innovations
The next generation of Chase phishing email scams will likely leverage advancements in AI and machine learning to create even more convincing impersonations. Deepfake technology, for example, could enable scammers to generate hyper-realistic voice messages or video calls from what appears to be a Chase representative. Similarly, AI-driven email composition tools will allow scammers to craft messages that adapt in real-time based on a victim’s responses, making them nearly indistinguishable from legitimate communications. The rise of quantum computing may also pose new challenges, as it could break traditional encryption methods, making it easier for scammers to intercept secure communications.
On the defensive side, innovations like behavioral biometrics—where systems analyze typing patterns, mouse movements, and other user behaviors to detect anomalies—could become standard in banking security. Additionally, the adoption of blockchain-based identity verification may reduce reliance on traditional credentials, making phishing attempts less effective. However, the arms race between scammers and security experts will continue, necessitating constant vigilance. Staying ahead of these trends requires a combination of technological safeguards and user education, ensuring that customers remain the last line of defense against evolving Chase phishing email scams.
Conclusion
The threat of Chase phishing email scams is not going away—it’s evolving. What was once a simple scam relying on poor grammar and obvious fake links has transformed into a sophisticated, multi-layered attack that exploits psychology, technology, and human error. The good news is that awareness and proactive habits can neutralize these threats. By recognizing the warning signs—such as urgent language, unexpected requests for personal information, or suspicious links—users can significantly reduce their risk of falling victim. Additionally, leveraging tools like Chase’s built-in security features, such as transaction alerts and multi-factor authentication, adds an extra layer of protection.
Ultimately, the battle against phishing scams is a shared responsibility between financial institutions and their customers. Chase invests heavily in security infrastructure, but the final barrier is the individual’s ability to spot Chase phishing email scams before they succeed. The key takeaway is simple: stay informed, verify everything, and never assume an email is legitimate just because it looks official. In a digital landscape where scammers are constantly refining their tactics, vigilance remains the most powerful tool in the fight against fraud.
Comprehensive FAQs
Q: What are the most common red flags in a Chase phishing email?
A: The top red flags include urgent language demanding immediate action, generic greetings (e.g., "Dear Customer"), misspelled Chase URLs (e.g., chase-secure-login.net instead of chase.com), requests for sensitive information via email, and unexpected attachments or links. Always hover over links to check the destination URL before clicking.
Q: Can Chase ever ask for my password or PIN via email?
A: No. Chase will never ask for your full password, PIN, or Social Security number via email. If you receive such a request, it’s a scam. Legitimate communications from Chase may ask for partial information (e.g., last four digits of a card) for verification, but never full credentials.
Q: What should I do if I’ve already clicked a suspicious link in a Chase phishing email?
A: Act immediately by changing your Chase password, enabling multi-factor authentication, and reviewing recent transactions for unauthorized activity. Contact Chase’s official customer service (using the number on the back of your card or the verified Chase website) to report the incident and request a security freeze on your account.
Q: How can I verify if an email is truly from Chase?
A: Check the email address for typos or unfamiliar domains, look for Chase’s official logo and branding, and avoid clicking any links. Instead, manually type chase.com into your browser and navigate to the relevant section (e.g., "Security Alerts") to verify the claim. Chase will never send urgent requests via email alone.
Q: Are there tools or apps that can help detect Chase phishing scams?
A: Yes. Use email security tools like MailGuard, Proofpoint, or Chase’s own fraud alerts to filter suspicious messages. Browser extensions like Netcraft Extension can reveal hidden details about websites, and Chase’s mobile app includes built-in security features to flag unusual activity. Additionally, enable transaction alerts to catch fraudulent charges early.
Q: What’s the best way to report a Chase phishing email scam?
A: Forward the email to phishing@chase.com and report it to the FTC at reportfraud.ftc.gov. For immediate action, contact Chase’s fraud department at the number on the back of your card. If you suspect identity theft, file a report with the FTC Identity Theft Affidavit and consider placing a fraud alert on your credit reports.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Filmfestivalcircuit.