How Forward Proxy vs Reverse Proxy Shapes Modern Web Security
The internet’s invisible gatekeepers—forward proxy vs reverse proxy—operate in silent opposition, each serving distinct roles in the digital ecosystem. One masks identities at the edge of networks, while the other shields servers from direct exposure, yet both are fundamental to how data traverses the web. Their interplay defines everything from corporate anonymity to high-traffic website resilience, yet most users remain oblivious to the architectural divide that separates them.
At their core, these proxy systems represent a paradox: forward proxies act as intermediaries for clients seeking to conceal their requests, whereas reverse proxies intercept traffic destined for servers, filtering and optimizing it before delivery. The distinction isn’t merely semantic; it dictates security posture, performance tuning, and even compliance strategies. Misconfigured deployments can expose vulnerabilities, while optimized setups become the backbone of scalable, secure digital operations.
The stakes are higher than ever. As cyber threats evolve and cloud architectures dominate, understanding whether to implement a forward proxy vs reverse proxy—or both—has become a strategic imperative for IT teams. The wrong choice can lead to bottlenecks, data leaks, or service disruptions, while the right configuration enables seamless scalability and fortified defenses.

The Complete Overview of Forward Proxy vs Reverse Proxy
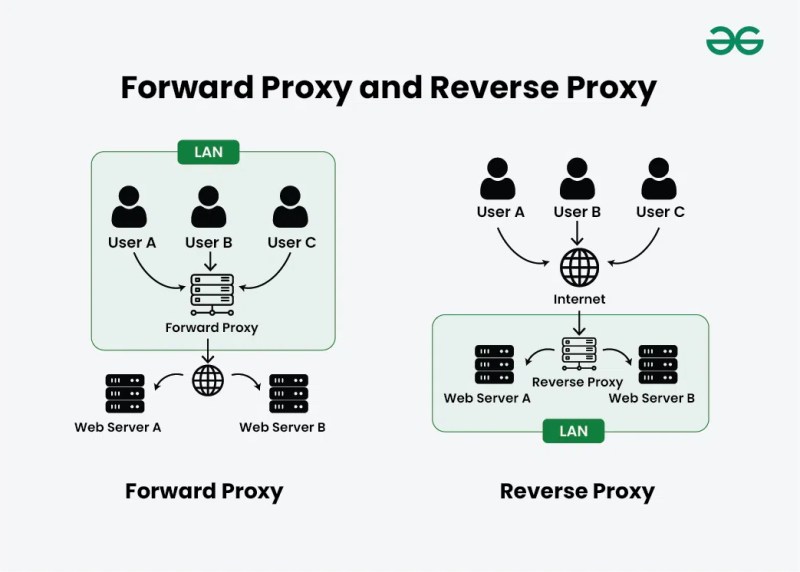
The terms forward proxy and reverse proxy describe two fundamentally different proxy architectures, each solving distinct problems in network communication. A forward proxy sits between clients and external servers, acting as a relay that obscures the origin IP of requests—commonly used for anonymity, content filtering, or bypassing geo-restrictions. In contrast, a reverse proxy positions itself in front of web servers, accepting incoming traffic on behalf of those servers, handling SSL termination, load balancing, and caching to enhance performance and security.While both systems route traffic, their operational contexts differ sharply. Forward proxies are client-side tools, often deployed in corporate networks or by individual users to access restricted content or protect privacy. Reverse proxies, however, are server-side components, typically managed by hosting providers or enterprises to distribute traffic, mitigate DDoS attacks, or simplify backend management. The choice between them hinges on whether the priority is client anonymity or server protection—though hybrid setups are increasingly common in complex infrastructures.
Historical Background and Evolution
The concept of proxy servers emerged in the early 1990s as a solution to the burgeoning challenges of internet scalability and censorship. Forward proxies were among the first to gain traction, deployed by universities and corporations to cache web content, reduce bandwidth costs, and enforce access controls. Their anonymizing capabilities also made them tools of resistance in regions with heavy internet restrictions, a role they retain today in privacy-focused applications like Tor or VPNs.Reverse proxies, by contrast, evolved alongside the rise of high-traffic websites in the late 1990s and early 2000s. As e-commerce and content-heavy platforms strained under direct client-server connections, reverse proxies like Squid and later Nginx became essential for load distribution, SSL offloading, and static content delivery. Their integration with CDNs further cemented their role in modern web architectures, where performance and security are non-negotiable.
Core Mechanisms: How It Works
A forward proxy operates by intercepting client requests before they reach their intended destination. When a user configures their browser or application to route traffic through a forward proxy (e.g., `proxy.example.com:8080`), all outbound connections appear to originate from the proxy’s IP address. This mechanism enables anonymity, bypasses regional blocks, and allows centralized logging or filtering of outgoing traffic. The proxy fetches the requested resource from the external server and forwards the response back to the client, effectively acting as a middleman.Table of Contents
- The Complete Overview of Forward Proxy vs Reverse Proxy
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Can a single proxy server function as both a forward and reverse proxy?
- Q: How do forward proxies impact SEO and web scraping?
- Q: Are reverse proxies vulnerable to cache poisoning?
- Q: Can forward proxies improve internet speeds?
- Q: What’s the difference between a proxy and a VPN?
- Q: How do reverse proxies handle WebSocket connections?
- Q: Are there legal risks associated with using forward proxies?
Reverse proxies function in reverse: they receive incoming requests destined for a web server and decide how to handle them. Instead of hiding the client, they hide the server, accepting connections on its behalf. The reverse proxy can terminate SSL/TLS connections, compress responses, cache static assets, or distribute requests across multiple backend servers using algorithms like round-robin or least connections. This not only improves performance but also shields servers from direct exposure to malicious traffic, such as SQL injection or DDoS attacks.
Key Benefits and Crucial Impact
The strategic deployment of forward proxy vs reverse proxy systems has become a cornerstone of contemporary cybersecurity and web operations. Organizations leverage these tools to balance privacy, performance, and compliance—each serving a unique niche in the broader landscape of network infrastructure. The distinction between the two isn’t just technical; it’s operational, influencing everything from user experience to regulatory adherence.At its best, a well-configured proxy setup can transform a vulnerable system into a fortress. Forward proxies, for instance, are indispensable in corporate environments where employees must access restricted resources without exposing internal IPs. Reverse proxies, meanwhile, enable enterprises to scale dynamically, handle surges in traffic, and enforce granular security policies at the perimeter. The synergy between the two—when applied thoughtfully—creates a multi-layered defense that adapts to modern threats.
"Proxies are the unsung heroes of the internet’s infrastructure—silent enablers of both privacy and performance, yet their misuse can turn them into liabilities. The key lies in understanding their distinct roles and deploying them where they matter most." — Security Architect, Global Tech Firm (2024)
Major Advantages
- Anonymity and Privacy: Forward proxies mask client IPs, making them ideal for bypassing geo-restrictions, evading surveillance, or accessing censored content. They’re the backbone of privacy tools like Tor and corporate anonymity policies.
- Centralized Control: Both proxy types allow administrators to enforce policies (e.g., content filtering, bandwidth throttling) from a single point, simplifying compliance with regulations like GDPR or COPPA.
- Load Balancing and Scalability: Reverse proxies distribute traffic across multiple servers, preventing overload and enabling horizontal scaling—critical for SaaS platforms and high-traffic websites.
- Security Hardening: Reverse proxies act as a buffer against DDoS attacks, SQL injection, and other Layer 7 threats by inspecting and sanitizing incoming requests before they reach backend systems.
- Caching and Performance: Both proxy types can cache responses, reducing latency and server load. Reverse proxies, in particular, optimize dynamic content delivery by offloading SSL processing and compressing data.

Comparative Analysis
The choice between forward proxy vs reverse proxy hinges on operational goals, security requirements, and infrastructure design. Below is a direct comparison of their key attributes:| Criteria | Forward Proxy | Reverse Proxy |
|---|---|---|
| Primary Role | Client-side intermediary; hides client IP. | Server-side intermediary; hides server IP. |
| Deployment Location | Between client and external server (e.g., corporate network edge). | Between external clients and internal servers (e.g., web server perimeter). |
| Common Use Cases | Anonymity, content filtering, bypassing restrictions, privacy. | Load balancing, SSL termination, DDoS protection, caching. |
| Security Focus | Client protection (e.g., hiding internal IPs from external servers). | Server protection (e.g., shielding backend from malicious traffic). |
Future Trends and Innovations
The landscape of forward proxy vs reverse proxy technologies is evolving rapidly, driven by advancements in AI, edge computing, and zero-trust architectures. Forward proxies are increasingly integrating with decentralized networks, such as IPFS or blockchain-based anonymity tools, to enhance resilience against censorship. Meanwhile, reverse proxies are adopting machine learning to dynamically detect and mitigate sophisticated attacks, such as credential stuffing or API abuse.Another trend is the convergence of these proxies with service mesh architectures, where both forward and reverse proxy functions are embedded within microservices to enable granular traffic control. Additionally, the rise of edge computing is pushing reverse proxies closer to end-users, reducing latency for global applications. As quantum computing looms on the horizon, proxy systems may also incorporate post-quantum cryptography to future-proof SSL/TLS communications—a critical consideration for both forward and reverse proxy deployments.
Conclusion
The debate over forward proxy vs reverse proxy isn’t about which is superior but about recognizing their complementary roles in a secure, high-performance digital ecosystem. Forward proxies excel in scenarios demanding client anonymity or access control, while reverse proxies are indispensable for server-side optimization and threat mitigation. The most robust infrastructures often employ both, creating layered defenses that address the full spectrum of cybersecurity challenges.As networks grow more complex and threats more sophisticated, the ability to distinguish—and strategically deploy—these proxy types will define the resilience of modern systems. Whether shielding a user’s identity or fortifying a web application, the choice between forward proxy vs reverse proxy is less about technical preference and more about aligning architecture with operational objectives.
Comprehensive FAQs
Q: Can a single proxy server function as both a forward and reverse proxy?
A: Yes, certain proxy software like Nginx or HAProxy can be configured to act as either a forward or reverse proxy, depending on the traffic direction and use case. However, their roles remain distinct: the same server cannot simultaneously hide client IPs (forward) and server IPs (reverse) for the same request flow. Specialized setups may combine both functionalities in a layered architecture.
Q: How do forward proxies impact SEO and web scraping?
A: Forward proxies can both help and hinder SEO and scraping efforts. On one hand, they allow users to bypass IP-based blocks (e.g., Google’s anti-scraping measures) by rotating IPs. On the other, excessive proxy usage—especially with residential IPs—can trigger bot detection algorithms, leading to temporary bans. For SEO, proxies are neutral unless misused; for scraping, they’re essential but require careful IP rotation strategies to avoid detection.
Q: Are reverse proxies vulnerable to cache poisoning?
A: Yes, reverse proxies are susceptible to cache poisoning if not properly configured. Attackers may exploit vulnerabilities in the proxy’s caching logic to inject malicious content into cached responses, which are then served to legitimate users. Mitigation involves validating cache headers, implementing strict TTL policies, and using technologies like HTTP Strict Transport Security (HSTS) to prevent downgrade attacks.
Q: Can forward proxies improve internet speeds?
A: Indirectly, yes. Forward proxies can cache frequently accessed content (e.g., corporate intranet pages or popular websites), reducing bandwidth usage and latency for repeated requests. However, their primary function is not speed optimization—unlike reverse proxies, which are explicitly designed for performance tuning through compression, caching, and load balancing.
Q: What’s the difference between a proxy and a VPN?
A: While both proxies and VPNs route traffic through an intermediary, they differ in scope and security. A VPN encrypts all traffic from a device (including non-HTTP protocols like email or file transfers) and routes it through a secure tunnel, masking the entire device’s activity. A proxy, whether forward or reverse, typically handles only HTTP/HTTPS traffic and does not provide full-system encryption. VPNs are better for privacy; proxies are lighter and often used for specific tasks like content filtering or load balancing.
Q: How do reverse proxies handle WebSocket connections?
A: Modern reverse proxies like Nginx or Traefik support WebSocket traffic by forwarding persistent connections between clients and backend servers. They can terminate TLS for WebSocket connections, apply rate limiting, and even load balance WebSocket traffic across multiple instances. However, not all reverse proxies natively support WebSockets, so configuration may require additional modules or plugins.
Q: Are there legal risks associated with using forward proxies?
A: Yes, especially in jurisdictions with strict internet regulations. Using forward proxies to bypass geo-restrictions (e.g., accessing Netflix in a region where it’s blocked) may violate terms of service or local laws. Additionally, corporate use of unauthorized proxies can expose organizations to compliance risks under regulations like the Computer Fraud and Abuse Act (CFAA) or GDPR. Always ensure proxy usage aligns with legal and organizational policies.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Filmfestivalcircuit.