Mastering Tailscale Admin: The Definitive Guide to Secure Network Management
Tailscale admin isn’t just another network management tool—it’s a paradigm shift in how organizations approach secure remote access. Unlike legacy VPNs that demand complex configurations and persistent infrastructure, Tailscale leverages modern cryptography and peer-to-peer principles to create scalable, self-healing networks. The result? A tailscale admin experience that simplifies oversight while enhancing security, making it indispensable for teams balancing agility with compliance.
What sets Tailscale apart is its ability to abstract away the traditional VPN’s headaches—no static IPs, no firewall nightmares, and no reliance on centralized gateways. Instead, devices authenticate via ephemeral keys and route traffic through a global overlay network, all while maintaining end-to-end encryption. For administrators, this means fewer moving parts to monitor and fewer points of failure. Yet, the power lies in the details: understanding how to deploy, audit, and optimize a tailscale admin environment determines whether your network remains a force multiplier or a liability.
The stakes couldn’t be higher. As remote work becomes the norm and cloud sprawl accelerates, the need for a tailscale admin framework that scales without sacrificing visibility grows critical. Whether you’re managing a startup’s hybrid infrastructure or a Fortune 500’s distributed workforce, the decisions you make today—from access policies to device onboarding—will echo in your network’s resilience tomorrow.
The Complete Overview of Tailscale Admin
At its core, tailscale admin refers to the administrative practices and tools used to deploy, govern, and secure Tailscale networks. Unlike conventional VPNs that require dedicated hardware or cloud relays, Tailscale operates as a software-defined network, where each device becomes a node in a mesh topology. This design eliminates the need for a central server, reducing both operational overhead and single points of failure. For administrators, this translates to finer-grained control over device identities, traffic routing, and access policies—all without the complexity of traditional infrastructure.
The tailscale admin model thrives on three pillars: identity-based access, ephemeral networking, and automated compliance. Devices authenticate via short-lived certificates tied to user accounts or machine identities, ensuring that only authorized endpoints can join the network. Traffic flows directly between peers when possible, with fallback to Tailscale’s global relays only when necessary. Meanwhile, features like ACLs (Access Control Lists) and device tags allow admins to enforce granular policies—such as restricting certain devices to specific subnets or services—without manual intervention. This automation isn’t just convenient; it’s a necessity in environments where manual oversight would be unsustainable.
Historical Background and Evolution
The origins of Tailscale trace back to 2016, when its creators sought to solve the persistent challenges of remote access: latency, cost, and security. Traditional VPNs, while reliable, often required static IP allocations, dedicated hardware, or complex routing tables—all of which scaled poorly for distributed teams. Tailscale’s founders recognized that the internet’s underlying infrastructure (specifically, NAT traversal techniques like STUN and TURN) could be repurposed to create a more dynamic, peer-to-peer alternative. By 2018, the project emerged as an open-source tool, leveraging WireGuard’s high-performance encryption and the MagicDNS system to simplify device discovery.
Table of Contents
- The Complete Overview of Tailscale Admin
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: How does Tailscale admin handle multi-team environments?
- Q: Can Tailscale admin replace a corporate firewall?
- Q: What happens if a device’s Tailscale key is compromised?
- Q: How does Tailscale admin integrate with existing authentication systems?
- Q: Are there performance limitations with large-scale deployments?
- Q: Can Tailscale admin enforce granular application-level policies?
Today, tailscale admin has evolved into a full-fledged enterprise solution, with features like audit logging, SSO integration, and multi-team management. The shift from a developer-friendly tool to a production-grade platform reflects broader industry trends: the demand for zero-trust architectures and the need to replace legacy VPNs with solutions that align with modern DevOps workflows. Companies like GitLab and Notion now rely on Tailscale to connect thousands of devices globally, proving that tailscale admin isn’t just a niche experiment—it’s a scalable reality.
Core Mechanisms: How It Works
The magic of tailscale admin lies in its hybrid approach to networking. Under the hood, Tailscale combines WireGuard’s secure tunneling with a distributed coordination layer that handles device authentication and routing. When a device (e.g., a laptop or server) installs the Tailscale client, it generates a unique ephemeral key pair. This key is registered with Tailscale’s coordination servers, which then issue a short-lived certificate. The device’s public IP and port are dynamically mapped to a stable Tailscale IP (e.g., `100.x.y.z`), allowing seamless connectivity regardless of the underlying network topology.
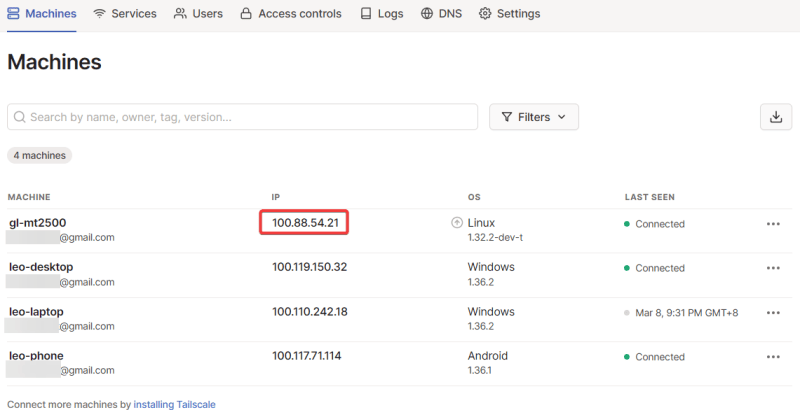
For admins, the tailscale admin dashboard provides visibility into this process, offering tools to monitor device health, inspect traffic flows, and enforce policies. ACLs, for example, can restrict access based on device tags (e.g., `team=engineering` or `role=ci-server`), while the `tailscale up` command allows for scripted deployments. The system’s reliance on ephemeral credentials means that even if a device’s key is compromised, it can’t be reused—unlike static credentials in traditional VPNs. This design ensures that tailscale admin isn’t just reactive but inherently secure by default.
Key Benefits and Crucial Impact
The value of tailscale admin becomes apparent when compared to the alternatives. Legacy VPNs often require dedicated hardware, static IP assignments, and manual routing configurations—all of which introduce friction for remote teams. Tailscale, by contrast, abstracts away these complexities, allowing admins to focus on policy enforcement rather than infrastructure maintenance. This shift isn’t just about convenience; it’s about enabling organizations to move faster while reducing the attack surface. For example, a company using tailscale admin can spin up a secure dev environment in minutes, whereas a traditional VPN might take days to provision.
Beyond efficiency, the tailscale admin model aligns with zero-trust principles by default. Every device must authenticate before joining the network, and traffic is encrypted end-to-end. There’s no reliance on a single gateway that could become a bottleneck or a target. Instead, the network self-heals: if a device’s connection drops, Tailscale automatically reroutes traffic through the nearest relay or peer. This resilience is particularly critical for global teams, where latency and reliability are non-negotiable.
"Tailscale admin isn’t just about connecting devices—it’s about redefining how networks are governed. The ability to enforce policies at the device level, without sacrificing performance, is a game-changer for security teams."
— Security Architect at a Top 10 Cloud Provider
Major Advantages
- Zero-Trust by Design: Every device authenticates via ephemeral keys, eliminating reliance on static credentials. Admins can revoke access instantly if a device is compromised.
- Global Scalability: Traffic routes directly between peers when possible, reducing latency. Tailscale’s relay network ensures connectivity even in restricted environments (e.g., behind NAT or firewalls).
- Simplified Administration: No need to manage VPN gateways or static IPs. The tailscale admin dashboard provides a unified view of all devices, their tags, and access policies.
- Automated Compliance: ACLs and audit logs make it easy to enforce company-wide policies (e.g., "only engineering laptops can access the CI server").
- Cost Efficiency: Eliminates the need for dedicated VPN hardware or cloud relays. The free tier supports up to 200 devices, with enterprise plans scaling as needed.

Comparative Analysis
To contextualize the tailscale admin approach, it’s useful to compare it with traditional VPNs and other zero-trust solutions. While tools like OpenVPN or WireGuard offer strong encryption, they often require manual configuration and lack built-in identity management. Cloud-based VPNs (e.g., AWS Client VPN) provide scalability but introduce vendor lock-in and higher costs. Tailscale strikes a balance: it retains WireGuard’s performance while adding a layer of abstraction that simplifies administration.
| Feature | Tailscale Admin | Traditional VPN (e.g., OpenVPN) | Cloud VPN (e.g., AWS Client VPN) |
|---|---|---|---|
| Authentication | Ephemeral keys + SSO/OAuth | Static credentials or certificates | IAM roles or SAML |
| Scalability | Peer-to-peer with relay fallback (supports 10,000+ devices) | Limited by gateway capacity | Depends on cloud provider quotas |
| Administration Overhead | Minimal (ACLs, tags, and dashboard-driven) | High (manual routing, IP management) | Moderate (IAM policies, VPC configurations) |
| Cost | Free for 200 devices; pay-as-you-grow | Hardware/licensing costs | Per-hour cloud charges |
Future Trends and Innovations
The tailscale admin landscape is poised for further evolution, driven by advancements in cryptography and network automation. One emerging trend is the integration of Tailscale with service meshes (e.g., Istio or Linkerd), enabling admins to extend zero-trust principles beyond device-level access to application-level policies. For example, a tailscale admin could soon enforce that only containers tagged `env=production` can communicate with a database, regardless of their underlying host.
Another frontier is AI-driven network optimization. Tailscale’s coordination servers could leverage machine learning to predict traffic patterns and dynamically adjust relay placements, further reducing latency for global teams. Additionally, as quantum computing looms, post-quantum cryptography (e.g., CRYSTALS-Kyber) may become a standard feature in tailscale admin deployments, ensuring long-term security. These innovations will solidify Tailscale’s position not just as a VPN alternative, but as a foundational layer for next-generation networks.

Conclusion
The rise of tailscale admin reflects a broader industry shift toward decentralized, identity-first networking. By eliminating the complexities of traditional VPNs, it empowers administrators to focus on security and scalability rather than infrastructure maintenance. The result is a network that’s not only easier to manage but also more resilient against modern threats. For organizations already grappling with remote work and cloud complexity, adopting a tailscale admin approach isn’t just an upgrade—it’s a strategic necessity.
As the tool matures, its integration with DevOps pipelines, CI/CD systems, and cloud-native architectures will further blur the line between networking and application delivery. The question for admins isn’t whether to adopt tailscale admin, but how to leverage it to future-proof their infrastructure. The answer lies in mastering its core principles: identity, automation, and peer-to-peer resilience.
Comprehensive FAQs
Q: How does Tailscale admin handle multi-team environments?
A: Tailscale supports multi-team setups via tailscale admin features like teams and ACLs. Admins can create separate teams (e.g., `marketing`, `engineering`) and assign devices to them using tags. ACLs then enforce isolation—e.g., preventing the `marketing` team from accessing `engineering` resources. Audit logs track all access attempts, ensuring compliance.
Q: Can Tailscale admin replace a corporate firewall?
A: While tailscale admin provides strong encryption and access controls, it’s not a direct replacement for a firewall. Tailscale secures traffic between devices but doesn’t filter or log inbound/outbound traffic at the network perimeter. For full firewall functionality, pair Tailscale with a next-gen firewall (e.g., Palo Alto or Cloudflare) that inspects Tailscale traffic.
Q: What happens if a device’s Tailscale key is compromised?
A: Tailscale’s ephemeral keys mitigate this risk. If a device’s key is stolen, admins can revoke it instantly via the tailscale admin dashboard or API. The device will fail authentication and be locked out. Additionally, Tailscale’s coordination servers rotate keys periodically, reducing the window for exploitation.
Q: How does Tailscale admin integrate with existing authentication systems?
A: Tailscale admin supports SSO via OAuth (e.g., Google, Okta, or Azure AD). Devices can authenticate using existing corporate credentials, streamlining onboarding. Admins can also enforce MFA for additional security. The integration is seamless: users log in once, and their Tailscale access is tied to their identity provider.
Q: Are there performance limitations with large-scale deployments?
A: Tailscale is designed for scale, with benchmarks showing stable performance up to 10,000+ devices. Traffic routes peer-to-peer by default, minimizing latency. For global teams, Tailscale’s relay network ensures connectivity even in restricted regions. However, admins should monitor bandwidth usage and adjust ACLs to optimize traffic flows (e.g., prioritizing critical services).
Q: Can Tailscale admin enforce granular application-level policies?
A: Currently, tailscale admin enforces policies at the device or subnet level (e.g., "allow `db-server` to access port 5432"). For application-level controls (e.g., restricting API access by user role), integrate Tailscale with a service mesh like Istio or a proxy like NGINX. These tools can layer additional policies on top of Tailscale’s network-level security.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Filmfestivalcircuit.