Location Permissions: Everything You Need to Navigate Privacy & Tech
The smartphone in your pocket knows more about your daily movements than your closest friends. Every time an app requests access to your location, it’s not just a prompt—it’s a negotiation over control of your digital footprint. Location permissions are the silent architecture of modern connectivity, enabling everything from ride-sharing to emergency services while raising critical questions about surveillance and autonomy. Ignore them at your peril: one misconfigured setting can turn a convenience into a vulnerability.
Behind the scenes, location permissions operate as a delicate balance between functionality and privacy. Developers rely on them to deliver hyper-personalized services, while regulators scramble to enforce boundaries in an era where geotagging can reveal sensitive patterns—from medical visits to political affiliations. The stakes are higher than ever, yet most users treat these permissions as checkboxes to dismiss. That oversight isn’t just careless; it’s a systemic gap in digital literacy.
The truth is, location permissions everything you need—whether you’re optimizing app performance, safeguarding personal data, or navigating the legal gray areas of tracking. What follows is a meticulous breakdown of how these systems function, their transformative impact, and the evolving landscape of user rights in a location-aware world.

The Complete Overview of Location Permissions
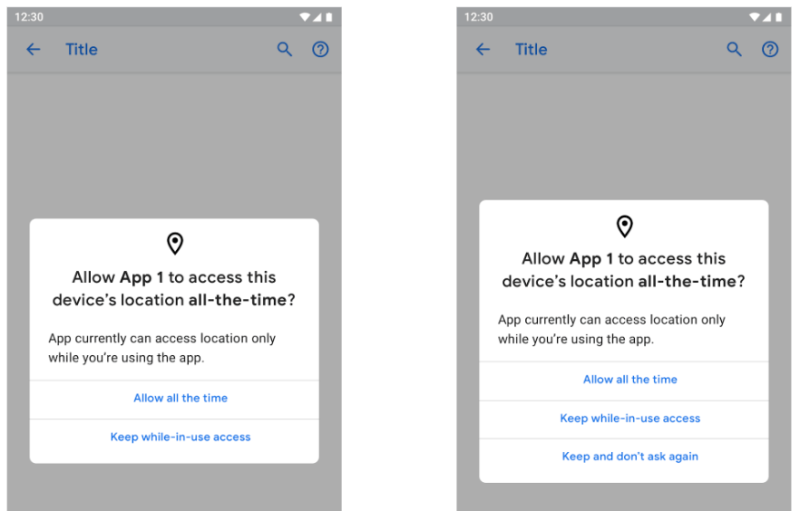
Location permissions are the gatekeepers of geospatial data access, determining which apps can pinpoint your whereabouts in real time or retrieve historical movement patterns. At their core, they function as a contractual agreement between users and developers, governed by platform-specific policies (e.g., Apple’s App Tracking Transparency or Android’s Location Permissions API). The request itself is deceptively simple: a pop-up asking for "always," "while using the app," or "deny" access. Beneath this interface lies a complex web of backend logic, where permissions are logged, shared with third parties, or exploited through loopholes like background tracking.The modern iteration of location permissions emerged from the convergence of GPS technology, mobile OS advancements, and the rise of location-based services (LBS) in the late 2000s. Early adopters like Foursquare and Google Maps demonstrated the commercial potential of geotagging, but they also exposed privacy flaws—most notably the 2010 revelation that Apple’s iOS was secretly transmitting users’ location data to its servers, even when apps were closed. This scandal forced Apple to overhaul its permission model, introducing granular controls that set the standard for competitors. Today, location permissions everything you need to understand how apps monetize your data, from targeted ads to insurance premiums based on driving habits.
Historical Background and Evolution
The concept of location tracking predates smartphones, tracing back to military and maritime navigation systems in the 20th century. However, the democratization of GPS in the 1990s—followed by its integration into consumer devices—accelerated the shift toward ubiquitous geolocation. The turning point came in 2007 with the iPhone’s launch, which embedded a GPS chip and sparked an arms race among tech giants to refine location-based services. By 2012, Google’s "Location History" feature became a privacy flashpoint, prompting lawsuits and regulatory scrutiny over whether users could opt out without sacrificing core functionality.Regulatory frameworks have struggled to keep pace. The European Union’s GDPR (2018) introduced stricter consent requirements, while the U.S. lacks federal legislation, leaving enforcement to state laws like California’s CCPA. Meanwhile, tech companies have weaponized ambiguity: terms of service often bury location-sharing clauses in dense legalese, and default settings frequently err on the side of data collection. The result? A fragmented ecosystem where location permissions everything you need to decipher who’s tracking you—and why.
Core Mechanisms: How It Works
Under the hood, location permissions rely on a trio of technologies: GPS (for precise outdoor coordinates), Wi-Fi/Bluetooth beacons (for indoor positioning), and cellular triangulation (as a fallback). When an app requests access, the OS triggers a permission dialog, but the actual data flow is more opaque. For example, an app granted "always" access can log your movements even when dormant, while "while using" permissions may still leak data via background processes. Developers often exploit these nuances: a weather app might ask for location to display forecasts, but it could also sell anonymized (or re-identified) movement data to advertisers.Table of Contents
- The Complete Overview of Location Permissions
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Can apps track my location even if I deny permission?
- Q: How do I revoke location access for an app?
- Q: Are there apps that don’t need location access?
- Q: Can my employer track my location through company devices?
- Q: What’s the difference between "always" and "while using" permissions?
- Q: How can I check if my location is being shared without my knowledge?
- Q: Do VPNs hide location tracking?
- Q: Are there legal consequences for apps misusing location data?
- Q: Can I opt out of location tracking entirely?
The mechanics extend to third-party integrations. Many apps delegate location services to SDKs (software development kits) like Google’s Location Services or Mapbox, which introduce additional layers of data handling. Worse, some permissions are invisible—such as those embedded in system-level APIs that apps use without explicit user consent. This opacity is why location permissions everything you need to audit your digital environment: a single app can trigger a cascade of tracking events across platforms.
Key Benefits and Crucial Impact
Location permissions are the linchpin of a $100+ billion industry built on geospatial intelligence. For consumers, they unlock conveniences like real-time navigation, contact tracing during pandemics, or location-based discounts. For businesses, they enable precision marketing, asset tracking, and operational efficiency. Yet the trade-offs are stark: studies show that 70% of users are unaware of how their location data is used post-consent, and 40% of apps request unnecessary permissions. The asymmetry between utility and risk is what makes this topic urgent.At its best, location permissions everything you need to balance innovation with individual rights. Consider emergency services: without location sharing, 911 calls would lack critical context. But at its worst, the system becomes a tool for exploitation—insurance companies denying claims based on "risky" movement patterns, or law enforcement agencies accessing location data without warrants. The tension between functionality and privacy isn’t theoretical; it’s a daily reality for billions.
"Location data is the most intimate form of personal information—it reveals not just where you are, but who you associate with, what you value, and when you’re vulnerable." — Alvaro Bedoya, Georgetown Law Professor
Major Advantages
- Enhanced User Experience: Apps like Waze or Yelp rely on location permissions to deliver hyper-relevant content, saving time and resources.
- Public Safety Net: Features like Apple’s Emergency SOS or Google’s Crash Detection depend on real-time location sharing to coordinate rescues.
- Economic Incentives: Location-based rewards (e.g., Starbucks app perks) create direct value for users while funding app development.
- Research and Development: Anonymized location data fuels urban planning, climate studies, and disease tracking (e.g., COVID-19 mobility reports).
- Regulatory Compliance: Properly configured permissions help businesses adhere to laws like GDPR, avoiding fines and reputational damage.
Comparative Analysis
| Platform | Key Differences in Location Permissions |
|---|---|
| iOS (Apple) | Stricter default denials; requires explicit user consent for tracking (ATT framework). Background location access is logged and auditable. |
| Android (Google) | More granular but less transparent; allows "approximate" location access (less precise). Background restrictions vary by OS version. |
| Web (JavaScript APIs) | No persistent permissions; requires active user interaction (e.g., browser dialog). Limited to GPS/Wi-Fi-based geolocation. |
| Third-Party SDKs | Often bypass native permission systems; may request location access on behalf of apps without clear disclosure. |
Future Trends and Innovations
The next frontier in location permissions lies in decentralized identity systems, where users could own and monetize their geospatial data via blockchain-based ledgers. Projects like Microsoft’s "Decentralized Identity" or the EU’s GAIA-X initiative aim to give individuals control over data sharing, but scalability remains a hurdle. Meanwhile, edge computing—processing location data locally on devices—could reduce reliance on cloud-based tracking, though it introduces new security challenges.Regulatory pressure will also reshape the landscape. Proposed laws like the U.S. ADPPA (American Data Privacy and Protection Act) could standardize location consent requirements, while AI-driven permission managers (e.g., apps that auto-block unnecessary requests) may empower users to take back control. One certainty is that location permissions everything you need to adapt to a future where geospatial data is both a commodity and a civil liberty.

Conclusion
Location permissions are not a technical detail—they’re a societal contract with profound implications for privacy, security, and equality. The systems governing them are evolving faster than public understanding, leaving users vulnerable to both corporate overreach and state surveillance. The good news? Awareness is the first line of defense. By scrutinizing app requests, leveraging platform tools (like iOS’s Privacy Report), and advocating for transparent policies, individuals can reclaim agency in a location-obsessed world.The message is clear: location permissions everything you need to navigate the digital age responsibly. The question is whether society will treat them as a feature—or a fundamental right.
Comprehensive FAQs
Q: Can apps track my location even if I deny permission?
Not directly, but some apps use workarounds like Wi-Fi/Bluetooth scanning or IP-based geolocation. Always check app reviews for reports of suspicious behavior.
Q: How do I revoke location access for an app?
On iOS: Settings > Privacy > Location Services > [App Name]. On Android: Settings > Apps > [App Name] > Permissions. Some apps may require a full uninstall to reset.
Q: Are there apps that don’t need location access?
Most do, but utilities like calculators, notes apps, or offline games typically don’t. Always question why an app requests location—if it’s unrelated to its core function, it’s a red flag.
Q: Can my employer track my location through company devices?
Yes, if they own the device or have explicit IT policies. Some companies use MDM (Mobile Device Management) tools to monitor location, often for "security" reasons. Review your workplace’s acceptable use policy.
Q: What’s the difference between "always" and "while using" permissions?
"Always" enables background tracking (e.g., fitness apps). "While using" restricts access to active sessions, though some apps may still log data via other means. Neither guarantees 100% privacy.
Q: How can I check if my location is being shared without my knowledge?
On iOS: Enable Settings > Privacy > Location Services > System Services > Significant Locations to audit stored data. On Android: Use third-party tools like NetGuard to monitor network-level location requests.
Q: Do VPNs hide location tracking?
VPNs mask your IP address but don’t stop GPS or Wi-Fi-based tracking. For true privacy, combine a VPN with location permission audits and offline modes.
Q: Are there legal consequences for apps misusing location data?
Under GDPR or CCPA, yes—fines up to 4% of global revenue. However, enforcement is inconsistent, and many apps operate in legal gray areas (e.g., sharing data with ad networks). Report violations to your regional data protection authority.
Q: Can I opt out of location tracking entirely?
Partially. Disable GPS/Wi-Fi scanning in Settings > Location**, but some services (like emergency calls) may still require basic geolocation. Balance is key.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Filmfestivalcircuit.