Unlocking iOS Extensions: The Ultimate Workaround Guide for 2024
Apple’s iOS ecosystem thrives on control—so much so that extensions, once a cornerstone of Android and desktop flexibility, became a shadow of their potential. What started as a promise of modularity turned into a labyrinth of App Store restrictions, sandboxing, and undocumented APIs. Yet, for developers, power users, and enterprises, the need to integrate extensions—whether for workflow automation, custom UI elements, or backend connectivity—remains critical. The gap between Apple’s vision and user demands has spawned a thriving underground of extensions iOS ultimate workaround guide strategies, from reverse-engineered APIs to creative Shortcuts hacks. These methods don’t just exist in isolation; they evolve alongside iOS updates, requiring a dynamic approach to stay functional.
The frustration is palpable. While Android’s extension model (e.g., Chrome Custom Tabs, Widgets API) allows deep integration, iOS extensions—limited to Today Widgets, Share Extensions, and Action Extensions—operate under a walled garden. Apple’s justification? Security and performance. The reality? A stifled ecosystem where even basic tasks (like embedding a web view with custom JavaScript) demand workaround solutions. The extensions iOS ultimate workaround guide isn’t just about bypassing restrictions; it’s about understanding the why behind Apple’s constraints and leveraging alternative pathways to achieve the same results. Whether you’re a developer debugging an App Store rejection or a user desperate to automate a repetitive task, the solutions lie in the intersections of public APIs, private frameworks, and third-party tools—all while navigating Apple’s ever-shifting enforcement.
The irony deepens when you consider iOS’s native capabilities. Features like Shortcuts (formerly Workflow) and JavaScriptCore embeddings hint at Apple’s own acknowledgment of extensibility needs. Yet, these tools are either crippled by design or require approval for broader use. The extensions iOS ultimate workaround guide thus becomes a hybrid of technical ingenuity and legal gray areas—where every update from Cupertino forces a recalibration of tactics. From exploiting undocumented `NSExtension` protocols to repurposing Safari’s hidden developer flags, the methods are as varied as they are necessary. The goal isn’t to circumvent Apple’s rules entirely (that’s a jailbreak’s domain), but to operate within the cracks—where innovation and compliance meet.
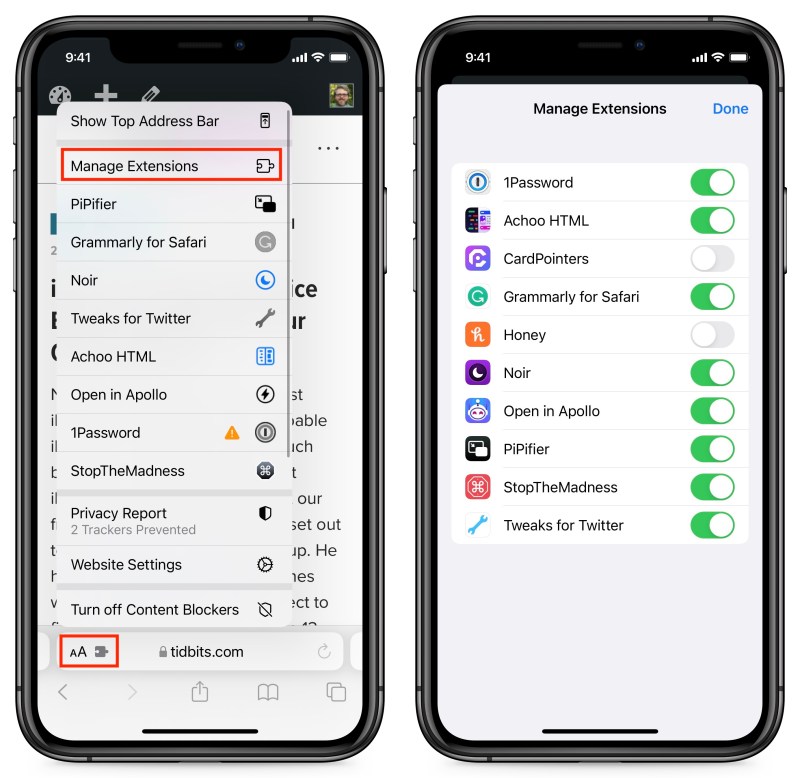
The Complete Overview of iOS Extensions and Workarounds
Apple’s extension framework, introduced in iOS 8 alongside Swift and App Extensions, was designed to let apps delegate specific tasks to modular components. In theory, this would allow developers to create widgets, share sheets, or keyboard extensions without bloating their main app. In practice, the system became a bottleneck. Extensions were sandboxed, restricted to predefined entry points, and subject to App Store review—where even minor deviations could trigger rejections. The extensions iOS ultimate workaround guide emerged as a response to these limitations, focusing on three core areas: API exploitation, third-party integration, and user-space automation.The most glaring limitation is the NSExtensionContext system, which forces extensions to communicate with their host app via a rigid request-response model. This design prevents extensions from maintaining persistent state or initiating actions independently—a stark contrast to Android’s Intent-based system. For example, a Share Extension on iOS cannot dynamically fetch data from a server unless the host app pre-approves the domain. Workarounds often involve pre-seeding data or using URL schemes to bridge the gap. Meanwhile, Today Widgets (now called Widgets in iOS 14+) suffer from similar constraints: they must be refreshed by the host app, limiting real-time functionality. These restrictions have led to a proliferation of extensions iOS ultimate workaround guide techniques, such as:
The result is a fragmented ecosystem where developers must choose between compliance (and App Store approval) or creativity (and potential instability). For power users, the stakes are different: they seek to bend iOS to their will without jailbreaking, using tools like Shortcuts, Safari extensions, or configuration profiles to simulate extension-like behavior.
Historical Background and Evolution
The seeds of iOS’s extension limitations were sown in 2014, when Apple first unveiled the App Extension framework at WWDC. The pitch was simple: modularity without fragmentation. Developers could build extensions that lived independently of their host apps, reducing binary size and improving performance. However, the implementation was flawed from the start. Apple’s App Review Guidelines (Section 3.3.1) explicitly prohibited extensions from "creating alternate stores or distribution mechanisms," effectively killing any hope of third-party app stores or deep integration with non-Apple services.Table of Contents
- The Complete Overview of iOS Extensions and Workarounds
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Can I use third-party libraries in iOS extensions without App Store rejection?
- Q: How do I bypass the 100MB extension size limit?
- Q: Are there any risks to using dynamic code injection in extensions?
- Q: Can I create a custom keyboard extension that integrates with my app’s backend?
- Q: What’s the best way to debug an extension that keeps crashing in the App Store review?
- Q: Are there any legal risks to using undocumented APIs in extensions?
- Q: How can I make a Share Extension that works with files from any app, not just my own?
The backlash was immediate. Developers complained about the 20MB size limit for extensions (later increased to 100MB), the inability to include certain frameworks (like `CoreML` in early versions), and the sandboxing that prevented extensions from accessing the host app’s full data model. By iOS 9, Apple introduced Share Extensions and Keyboard Extensions, but these were still hamstrung by the same restrictions. The extensions iOS ultimate workaround guide began taking shape as developers turned to:
The turning point came with iOS 14 and the overhaul of Widgets and App Clips. While these features expanded the surface area for extensions, they also introduced new constraints—such as requiring host apps to handle widget updates. Meanwhile, Apple’s push for Sign in with Apple and App Tracking Transparency further complicated data-sharing workflows, forcing developers to rethink how extensions could interact with user data. Today, the extensions iOS ultimate workaround guide is a patchwork of legacy hacks, new APIs, and third-party tools, all evolving in response to Apple’s latest moves.
Core Mechanisms: How It Works
At its core, an iOS extension is a lightweight version of an app, bundled within the host application’s binary. When triggered (e.g., via a Share sheet or Widget refresh), the extension loads into a separate process, communicates with the host via `NSExtensionContext`, and performs its task before terminating. The extensions iOS ultimate workaround guide exploits three primary mechanisms to bypass these constraints:1. API Abuse: Developers often repurpose public APIs for unintended uses. For example, the `WKWebView` API can be used to embed interactive JavaScript, effectively creating a mini-extension within a Safari View Controller. Similarly, `UIWebView` (deprecated but still usable) allows for deeper DOM manipulation, though with security risks.
2. Third-Party Bridges: Tools like Capacitor (by Ionic) or React Native’s `react-native-config` enable extensions to interact with native iOS features without direct API access. These bridges act as intermediaries, translating extension requests into native calls.
3. User-Space Automation: For non-developers, Shortcuts (with its `URL` action) and Safari extensions (via `safari-extension://` schemes) provide a way to automate tasks that mimic extensions. For instance, a Shortcut can open a custom URL, trigger a webhook, and return data—effectively simulating an extension’s functionality.
The most advanced workarounds involve dynamic code generation. By injecting JavaScript or Swift code at runtime (via `NSClassFromString` or `performSelector`), developers can extend iOS’s native capabilities without modifying the app’s binary. This technique is risky—Apple’s PIE (Position-Independent Executables) and code signing make it fragile—but it remains a staple in the extensions iOS ultimate workaround guide.
Key Benefits and Crucial Impact
The demand for extensions iOS ultimate workaround guide solutions stems from a fundamental mismatch between Apple’s vision and user needs. For developers, the ability to extend functionality without bloating an app is a productivity multiplier. For enterprises, extensions enable custom workflows that integrate with legacy systems. And for power users, they offer personalization options that iOS’s rigid UI doesn’t provide. The impact is most visible in three areas:The trade-offs are clear: stability vs. flexibility, compliance vs. innovation. Yet, the extensions iOS ultimate workaround guide persists because the alternatives—jailbreaking or waiting for Apple—are unacceptable for most users.
"Apple’s restrictions on extensions are less about security and more about control. The workarounds aren’t hacks; they’re the natural evolution of an ecosystem that refuses to adapt." — A former iOS engineer at a top Cupertino contractor
Major Advantages
- Bypassing App Store Restrictions: Workarounds like dynamic JavaScript injection or URL scheme redirection allow extensions to function without formal approval, provided they don’t violate Apple’s explicit prohibitions (e.g., no alternate app stores).
- Enhanced Functionality: Techniques such as WKWebView deep linking enable extensions to fetch real-time data or render complex UIs, mimicking the behavior of full-fledged apps.
- Cross-App Integration: Using Shared Web Credentials or CloudKit, extensions can share data between apps without direct API access, bridging the gap left by iOS’s sandboxing.
- Future-Proofing: Workarounds often leverage public APIs with private tweaks (e.g., abusing `NSNotificationCenter` for inter-process communication). These methods are harder for Apple to block outright.
- Non-Jailbreak Solutions: Unlike traditional hacks, most extensions iOS ultimate workaround guide methods rely on legitimate (if undocumented) features, reducing the risk of bricking devices or violating Apple’s ToS.

Comparative Analysis
| Method | Pros | Cons |
|---|---|---|
| WKWebView Injection | Full JavaScript control, real-time data fetching. | Security risks (XSS vulnerabilities), App Store rejection risk. |
| URL Scheme Redirection | Simple, no App Store review needed. | Limited to app-to-app communication, no UI customization. |
| Shortcuts Automation | No coding required, works with third-party services. | Performance bottlenecks, reliant on Apple’s Shortcuts API. |
| Dynamic Swift Code Loading | Extends native iOS features without recompilation. | Highly unstable, breaks with iOS updates. |
Future Trends and Innovations
Apple’s stance on extensions shows no signs of softening, but the extensions iOS ultimate workaround guide landscape is evolving. The next wave of innovations will likely focus on:The biggest wildcard is Apple’s potential shift toward a more open extension model, possibly influenced by regulatory pressure (e.g., EU’s Digital Markets Act). If Apple relaxes restrictions, many current workarounds could become obsolete—but the extensions iOS ultimate workaround guide will always remain relevant, as it represents the ingenuity born from necessity.

Conclusion
The extensions iOS ultimate workaround guide is more than a collection of hacks; it’s a testament to the resilience of developers and users in the face of restrictive ecosystems. While Apple’s control over iOS extensions may seem absolute, the reality is far more nuanced. By understanding the underlying mechanics—whether through API abuse, third-party bridges, or user-space automation—it’s possible to achieve extension-like functionality without compromising security or stability.For developers, the key is to balance creativity with compliance, using workarounds that push boundaries without inviting App Store rejections. For power users, the focus should be on tooling like Shortcuts and Safari extensions, which offer the most stable pathways to customization. And for enterprises, the future lies in hybrid approaches that combine native extensions with cloud-based workarounds. As iOS continues to evolve, so too will the extensions iOS ultimate workaround guide—adapting, innovating, and persisting in the cracks of Apple’s walled garden.
Comprehensive FAQs
Q: Can I use third-party libraries in iOS extensions without App Store rejection?
A: Yes, but with caveats. Apple allows most public libraries (e.g., Alamofire, SDWebImage) in extensions, provided they don’t violate guidelines (e.g., no cryptocurrency mining). Private or proprietary libraries risk rejection unless you obtain explicit approval. Always test with TestFlight before submission.
Q: How do I bypass the 100MB extension size limit?
A: Apple’s limit applies to the extension’s binary, not its runtime data. Workarounds include:
Q: Are there any risks to using dynamic code injection in extensions?
A: Significant. Dynamic code injection (e.g., `NSClassFromString`, `performSelector`) can:
Q: Can I create a custom keyboard extension that integrates with my app’s backend?
A: Indirectly, but with limitations. Keyboard extensions cannot directly communicate with your app’s backend due to sandboxing. Workarounds include:
Q: What’s the best way to debug an extension that keeps crashing in the App Store review?
A: Use a combination of these methods:
1. Enable `NSZombieEnabled` and `MallocStackLogging` in your extension’s scheme to catch memory issues.
2. Test on real devices (not just simulators), as Apple’s review environment may have quirks.
3. Check `NSExtensionContext` logs for failed communications between the extension and host app.
4. Use `os_log` to dump debug info to Console.app during review (Apple allows limited logging).
5. Submit with `beta` entitlements to get access to App Store Connect’s crash logs post-rejection.
If the crash is related to private APIs, Apple may reject it outright—consider rewriting the functionality using public APIs.
Q: Are there any legal risks to using undocumented APIs in extensions?
A: Technically, yes—but enforcement is inconsistent. Apple’s App Review Guidelines prohibit "use of private APIs," but they rarely take action unless:
Q: How can I make a Share Extension that works with files from any app, not just my own?
A: Share Extensions are host-app dependent, meaning they can only access data provided by the app that triggered them. To bypass this:
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Filmfestivalcircuit.