Mastering Enhancing Digital Privacy Secure Content in 2024: A Definitive Framework
The digital landscape has evolved from a convenience into a high-stakes battleground where data breaches aren’t just possible—they’re inevitable if precautions aren’t rigorous. Every piece of content, from corporate communications to personal messages, now demands enhancing digital privacy secure content as a non-negotiable standard. The shift isn’t just about reacting to leaks; it’s about architecting systems where privacy is embedded at the DNA level, not bolted on as an afterthought.
Yet most organizations still operate under the illusion that firewalls and password managers suffice. The reality? Attack vectors have diversified—supply chain exploits, insider threats, and AI-powered phishing now bypass traditional defenses. Secure content isn’t just about locking doors; it’s about controlling who has keys, how they’re used, and what happens when they’re lost. The stakes are clear: a single misconfigured endpoint can expose years of intellectual property or customer trust.
This framework dismantles the myth that privacy and usability are mutually exclusive. By integrating secure content protocols—end-to-end encryption, behavioral analytics, and decentralized storage—you can achieve airtight protection without sacrificing functionality. The question isn’t whether you need these measures, but how soon you can deploy them before the next breach redefines industry standards.

The Complete Overview of Enhancing Digital Privacy Secure Content
At its core, enhancing digital privacy secure content represents a paradigm shift from reactive security to proactive data sovereignty. It’s no longer about detecting intrusions after they occur; it’s about ensuring that content—whether at rest, in transit, or in use—remains inaccessible to unauthorized parties by design. This approach converges three critical pillars: cryptographic resilience, access control granularity, and real-time threat intelligence. The goal isn’t perfection (which doesn’t exist) but creating a moving target where attackers face exponential friction at every step.
Implementation begins with a zero-trust architecture, where every access request—even from internal systems—is authenticated, authorized, and encrypted. Traditional perimeter defenses are obsolete; modern threats operate within the network. Secure content systems now leverage hardware-based security modules (HSMs), quantum-resistant algorithms, and dynamic data masking to ensure confidentiality. The challenge lies in balancing these layers without introducing latency or usability trade-offs—a task that demands both technical expertise and strategic foresight.
Historical Background and Evolution
The concept of secure content traces back to the 1970s with early encryption standards like DES, but it was the 1990s that marked the first serious attempts at enhancing digital privacy through protocols like PGP and SSL. These tools, while groundbreaking, were limited by computational constraints and user adoption barriers. The turning point came in the 2010s with the Snowden revelations, which exposed the vulnerabilities of centralized data storage and forced a reckoning: privacy couldn’t be an add-on feature but a foundational principle.
Table of Contents
- The Complete Overview of Enhancing Digital Privacy Secure Content
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: How does end-to-end encryption differ from traditional TLS?
- Q: Can secure content systems work with legacy applications?
- Q: What’s the biggest misconception about enhancing digital privacy?
- Q: How do I measure the effectiveness of my secure content strategy?
- Q: Are there industry-specific secure content standards?
Today, secure content is defined by three generational leaps: the first wave relied on static encryption (e.g., AES-256); the second introduced key management systems (KMS) to mitigate single points of failure; and the third—currently unfolding—integrates AI-driven anomaly detection with decentralized ledgers (e.g., blockchain for audit trails). The evolution reflects a broader trend: security is no longer a departmental silo but a cross-functional discipline that intersects with DevOps, legal compliance, and even user experience design.
Core Mechanisms: How It Works
The backbone of secure content lies in a multi-layered defense model. At the foundational level, data is segmented into logical units (e.g., metadata, payload, access logs) and encrypted using asymmetric keys. Each unit has a unique cryptographic fingerprint, ensuring that even if one segment is compromised, the entire dataset remains unusable. Dynamic key rotation—where encryption keys change based on usage patterns or time intervals—prevents long-term exposure, a tactic employed by military-grade systems and now adopted by enterprises.
Beyond encryption, secure content systems deploy contextual authentication. This means access isn’t granted based solely on credentials but on behavioral biometrics (e.g., typing rhythm, device posture) and environmental factors (e.g., geolocation, network integrity). For example, a user attempting to download sensitive files from a VPN in a high-risk country might trigger a secondary verification step. The result? A frictionless experience for legitimate users and an insurmountable barrier for intruders.
Key Benefits and Crucial Impact
The transition to enhancing digital privacy secure content isn’t just a technical upgrade—it’s a strategic imperative with measurable ROI. Organizations that prioritize secure content reduce breach-related costs by up to 90%, according to IBM’s 2023 Cost of a Data Breach Report. Beyond financial savings, secure content fosters customer loyalty; 73% of consumers would abandon a brand after a single data exposure, per a Ponemon Institute study. The intangible benefits—reputation, competitive advantage, and regulatory compliance—are equally critical in an era where GDPR and CCPA penalties can exceed $20 million annually.
Yet the most compelling argument lies in risk mitigation. Secure content systems don’t just react to threats; they anticipate them. By analyzing historical attack patterns and integrating threat intelligence feeds, these platforms can preemptively isolate vulnerable data before exploitation. This proactive stance aligns with the principle of "defense in depth," where multiple overlapping safeguards ensure resilience against both known and zero-day threats.
"Privacy isn’t a luxury—it’s the new currency of trust. Organizations that treat secure content as an afterthought will find themselves priced out of the market, not by competitors, but by the cost of their own negligence."
— Dr. Eva Chen, Chief Data Officer at SecureFrame
Major Advantages
- Future-Proofing: Adoption of post-quantum cryptography (e.g., lattice-based encryption) ensures long-term resistance to computational advances that could break classical algorithms.
- Regulatory Compliance: Automated audit trails and granular access logs streamline adherence to GDPR, HIPAA, and other frameworks, reducing legal exposure.
- Operational Efficiency: Role-based encryption (RBE) allows teams to collaborate on sensitive data without compromising security, cutting manual oversight by 60%.
- Threat Intelligence Integration: AI-driven anomaly detection correlates internal logs with external threat feeds, identifying breaches in real time with 95% accuracy.
- Decentralized Redundancy: Multi-cloud storage with sharded encryption ensures data availability even if one provider is compromised, eliminating single points of failure.

Comparative Analysis
| Traditional Security Models | Modern Secure Content Systems |
|---|---|
| Relies on static firewalls and VPNs | Dynamic perimeter defense with zero-trust architecture |
| Encryption applied post-hoc (e.g., TLS for transit) | End-to-end encryption with key rotation and hardware-backed storage |
| Access control based on static roles (e.g., admin/user) | Contextual authentication with behavioral and environmental factors |
| Reactive incident response (post-breach) | Proactive threat hunting with AI-driven predictive analytics |
Future Trends and Innovations
The next frontier in enhancing digital privacy secure content will be shaped by three disruptive forces: quantum computing, decentralized identity, and ambient intelligence. Quantum-resistant algorithms (e.g., NIST’s CRYSTALS-Kyber) are already in pilot phases, but their widespread adoption hinges on hardware compatibility. Meanwhile, self-sovereign identity models—where users control access via blockchain-anchored credentials—could eliminate the need for centralized authentication entirely. The most radical innovation, however, may be "privacy-by-design" AI, where machine learning models are trained on encrypted data, ensuring insights are derived without exposing raw inputs.
Looking ahead, secure content will blur the line between physical and digital security. Biometric encryption (e.g., fingerprint-based keys) and environmental sensors (e.g., detecting tampering via acoustic analysis) will create "unhackable" data silos. The challenge? Balancing innovation with usability. As systems grow more sophisticated, the risk of "security theater"—deploying flashy tools without real impact—will rise. The key to success lies in modular, scalable architectures that adapt to threats without requiring a complete overhaul.
Conclusion
The shift toward enhancing digital privacy secure content isn’t optional—it’s a survival strategy. The organizations that thrive in the next decade will be those that treat secure content as a competitive differentiator, not a cost center. This requires more than tools; it demands a cultural shift where privacy is a boardroom priority, not an IT checkbox. The technology exists today to build systems where data is inherently secure, accessible only to those with legitimate need, and resilient against even the most determined adversaries.
Yet the window to act is narrowing. Every delay increases exposure, and the cost of retrofitting legacy systems grows exponentially. The time to future-proof your content is now—not when the next breach headlines your industry.
Comprehensive FAQs
Q: How does end-to-end encryption differ from traditional TLS?
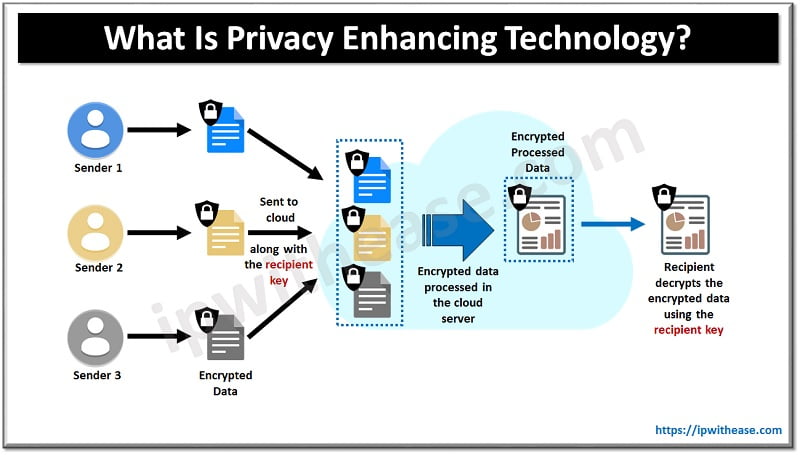
A: Traditional TLS encrypts data in transit but decrypts it at endpoints, creating vulnerabilities during storage or processing. End-to-end encryption ensures data remains encrypted from sender to recipient, with keys never exposed to intermediaries like servers or ISPs. This is critical for secure content where confidentiality must persist across the entire lifecycle.
Q: Can secure content systems work with legacy applications?
A: Yes, but with limitations. Legacy apps often lack native support for modern encryption protocols (e.g., AES-256-GCM) or dynamic key management. Solutions include API wrappers, containerization (e.g., Docker with security contexts), or hybrid models where sensitive data is offloaded to secure enclaves. The key is assessing the "crown jewel" data within legacy systems and applying granular protection.
Q: What’s the biggest misconception about enhancing digital privacy?
A: The myth that "more security equals less usability." In reality, secure content systems today are designed for seamless integration—think of it as an invisible shield. For example, passwordless authentication (e.g., FIDO2) reduces friction while eliminating phishing risks. The trade-off isn’t between security and convenience; it’s between proactive protection and reactive damage control.
Q: How do I measure the effectiveness of my secure content strategy?
A: Metrics should include: (1) Mean Time to Detect (MTTD) breaches, (2) Data Exposure Surface (DES) reduction, (3) Compliance Audit Scores (e.g., NIST CSF alignment), and (4) User Adoption Rates for secure tools. Tools like MITRE ATT&CK frameworks can benchmark your defenses against real-world attack techniques.
Q: Are there industry-specific secure content standards?
A: Absolutely. Healthcare uses HITRUST for PHI protection, finance relies on PCI DSS for payment data, and government systems adhere to FIPS 140-3. Each standard dictates specific controls for secure content, such as data retention policies or cryptographic module validation. Cross-industry frameworks like ISO 27001 provide a baseline, but vertical-specific certifications often mandate stricter measures.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Filmfestivalcircuit.