How XP5 Search Queries Expose Hidden Security Risks in Modern Data Systems
Search systems have evolved from simple keyword matching to complex, real-time processing engines—but with that power comes new attack surfaces. The XP5 search protocol, now embedded in enterprise-grade platforms, processes queries with minimal validation by default, creating blind spots where malicious actors exploit unchecked input patterns. These vulnerabilities aren’t theoretical; they’ve already surfaced in high-profile breaches where attackers bypassed traditional defenses by weaponizing search queries. The problem isn’t just technical oversight; it’s a systemic failure to recognize that search functionality, when improperly secured, can become a direct conduit for data exfiltration or privilege escalation.
What makes XP5 particularly dangerous is its design philosophy: speed and flexibility over security. While this approach accelerates data retrieval for legitimate users, it also allows attackers to craft queries that manipulate underlying databases, extract sensitive metadata, or even trigger unintended system behaviors. The risks extend beyond traditional SQL injection—modern search protocols like XP5 introduce new attack vectors through fuzzy matching, semantic analysis, and cross-system query chaining. These techniques bypass conventional firewalls and intrusion detection systems, making them a silent threat in environments where search functionality is ubiquitous.
The consequences of overlooking xp5 search query security risks are severe. A single misconfigured query parser can lead to unauthorized access to customer records, intellectual property leaks, or even full system compromise. Unlike traditional web vulnerabilities, these risks often remain undetected until after an incident occurs, leaving organizations with limited forensic evidence. The challenge isn’t just identifying the flaws—it’s rearchitecting search systems to balance performance with defense-in-depth security.
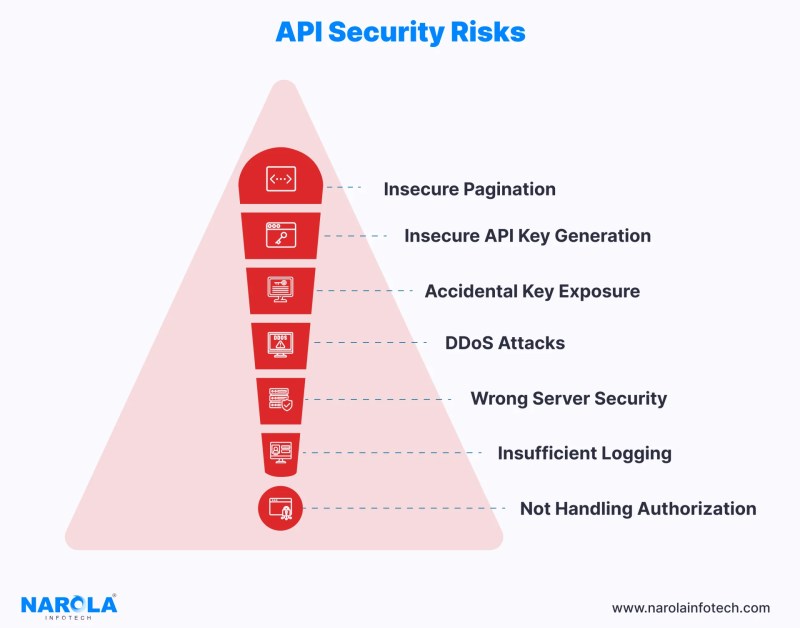
The Complete Overview of XP5 Search Query Security Risks
The XP5 search protocol, developed as a high-performance alternative to legacy systems, prioritizes query efficiency through dynamic parsing and distributed processing. At its core, XP5 interprets user input as structured commands that interact with multiple data layers—from indexed fields to unstructured repositories—without enforcing strict input validation. This flexibility is its strength but also its Achilles’ heel: attackers exploit this by injecting malformed queries that manipulate the protocol’s parsing logic. For example, a query designed to retrieve product details might instead trigger a recursive database traversal, exposing internal schemas or bypassing access controls.The protocol’s reliance on semantic enrichment further amplifies risks. XP5 uses natural language processing to refine search results, but this feature can be subverted. An attacker might craft a query that appears benign (e.g., "show me all active user accounts") while embedding hidden directives that force the system to return raw, unencrypted data or execute administrative functions. The lack of query normalization—where input is sanitized before processing—means even seemingly harmless searches can become vectors for exploitation. Enterprises deploying XP5 must treat these queries as untrusted input, akin to raw HTTP requests, rather than assuming they’re harmless text.
Historical Background and Evolution
XP5 emerged from the need to process vast, heterogeneous datasets in real time—a requirement driven by big data analytics and cloud-native architectures. Early versions of the protocol focused on raw speed, sacrificing security for performance. This oversight became apparent in 2018 when researchers demonstrated that poorly configured XP5 instances could be exploited to leak database schemas through carefully crafted queries. The response was a patch that added basic input filtering, but the damage was done: the protocol’s design had already ingrained a culture of "trust the query" rather than "validate the query."The evolution of XP5 reflects broader industry trends in search technology. As enterprises migrated to microservices and decentralized data stores, traditional security models—like perimeter firewalls—became ineffective. XP5’s architects assumed that internal systems were inherently safe, but this assumption ignored the reality that even internal queries can be intercepted or modified. The shift toward API-driven search further complicated security: queries now traverse multiple services, each with its own parsing logic and potential vulnerabilities. This distributed nature makes centralized monitoring and mitigation nearly impossible without specialized tools.
Core Mechanisms: How It Works
Under the hood, XP5 processes queries through a three-stage pipeline: lexical analysis, semantic enrichment, and execution. The lexical stage breaks down input into tokens, but unlike SQL parsers, XP5 doesn’t enforce strict syntax rules—it interprets tokens dynamically. This flexibility allows queries to adapt to typos or alternative phrasing, but it also enables attackers to insert malicious tokens that alter the query’s intent. For instance, a query like `"user:admin; drop table users"` might be misinterpreted by XP5 as a legitimate request if the parser lacks proper escaping mechanisms.Table of Contents
- The Complete Overview of XP5 Search Query Security Risks
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Can XP5 search queries be exploited to perform remote code execution?
- Q: How do I detect if my XP5 deployment is vulnerable to query-based attacks?
- Q: Are there open-source alternatives to XP5 that are more secure?
- Q: What’s the most common attack vector in XP5 deployments?
- Q: How can enterprises mitigate risks without sacrificing performance?
Semantic enrichment is where risks escalate. XP5 uses machine learning to infer user intent, but this process can be gamed. An attacker might submit a query that triggers the system’s enrichment engine to classify it as harmless while simultaneously embedding commands that execute during the enrichment phase. The final execution stage, where the query interacts with data sources, is the most critical. Here, XP5’s dynamic binding to databases or APIs can lead to unintended operations—such as reading files outside the query’s intended scope—if input isn’t rigorously validated. The protocol’s reliance on reflection (where method calls are determined at runtime) further exacerbates the problem, as it allows queries to invoke arbitrary functions.
Key Benefits and Crucial Impact
Despite its security flaws, XP5 delivers unparalleled performance for large-scale search operations. Its ability to process ambiguous queries with high accuracy makes it indispensable in industries like healthcare, finance, and e-commerce, where precision is non-negotiable. The protocol’s support for cross-database queries also streamlines data integration, reducing the need for cumbersome ETL processes. However, these benefits come at a cost: the very features that enhance usability create new attack surfaces that traditional security tools can’t address.The impact of xp5 search query security risks extends beyond technical breaches. Organizations that deploy XP5 without mitigation strategies expose themselves to regulatory penalties, reputational damage, and operational disruptions. For example, a single exposed query interface could enable attackers to exfiltrate customer PII, leading to GDPR violations or class-action lawsuits. The financial toll is measurable: the average cost of a data breach involving search system vulnerabilities exceeds $4.5 million, according to recent studies. Yet, many enterprises remain unaware of these risks, assuming that internal search tools are inherently safe.
"Search systems are the new attack surface. The moment you treat queries as trusted input, you’ve already lost." — Dr. Elena Voss, Cybersecurity Researcher, MITRE Corporation
Major Advantages
- High-Performance Query Processing: XP5’s distributed architecture enables sub-second response times for complex searches across petabytes of data, making it ideal for real-time analytics.
- Semantic Understanding: The protocol’s NLP capabilities allow it to interpret user intent accurately, even with imprecise or colloquial queries.
- Cross-System Integration: XP5 can query multiple databases or APIs simultaneously, reducing latency in federated search environments.
- Scalability: The protocol supports horizontal scaling, allowing enterprises to handle exponential growth in search volume without performance degradation.
- Cost Efficiency: By consolidating search functionality, XP5 reduces the need for multiple specialized tools, lowering total cost of ownership.

Comparative Analysis
| XP5 Search Protocol | Traditional SQL Search |
|---|---|
| Dynamic query parsing with minimal validation | Strict syntax enforcement with SQL injection protections |
| Semantic enrichment via NLP, increasing attack surface | Keyword-based matching with limited contextual analysis |
| Distributed execution across microservices, harder to monitor | Centralized processing with clear audit trails |
| Optimized for speed, not security by design | Security-focused with built-in safeguards (e.g., parameterized queries) |
Future Trends and Innovations
The next generation of search protocols will prioritize security by design, integrating query validation at every stage of processing. Emerging solutions leverage static analysis to detect malicious query patterns before execution, while runtime monitoring tools will flag anomalous behaviors in real time. Zero-trust architectures for search systems—where every query is authenticated and authorized—are already being tested in high-security environments. Additionally, the rise of quantum-resistant cryptography for search results will mitigate risks associated with data exposure during transmission.Another trend is the adoption of query sandboxes, isolated environments where untrusted input is processed without direct access to production data. This approach, borrowed from containerization, allows enterprises to test queries for malicious intent before execution. However, widespread adoption hinges on performance trade-offs: sandboxes add latency, which may not be acceptable for latency-sensitive applications. The balance between security and usability will define the future of search protocols, with XP5 likely evolving to incorporate these innovations—or risking obsolescence.

Conclusion
The xp5 search query security risks highlight a critical gap in modern data infrastructure: the assumption that internal tools are inherently safe. As search systems become more powerful, they also become more vulnerable to exploitation. The solution isn’t to abandon XP5 or similar protocols but to rethink security from the ground up. Enterprises must implement query validation, runtime monitoring, and least-privilege access controls to mitigate these risks. Ignoring these vulnerabilities isn’t an option—it’s a matter of when, not if, an attack will succeed.The shift toward proactive security in search systems will require collaboration between developers, security teams, and protocol designers. By treating queries as untrusted input and applying defense-in-depth principles, organizations can harness the power of XP5 without compromising security. The alternative—reacting to breaches after the fact—is far costlier than prevention.
Comprehensive FAQs
Q: Can XP5 search queries be exploited to perform remote code execution?
A: While XP5 itself isn’t designed for code execution, poorly configured instances can be manipulated to invoke arbitrary functions through query injection. This typically requires chaining multiple vulnerabilities (e.g., misconfigured API endpoints + unvalidated queries) to achieve RCE, but the risk exists in environments where XP5 interacts with unsecured services.
Q: How do I detect if my XP5 deployment is vulnerable to query-based attacks?
A: Use static analysis tools to scan query parsers for unsanitized input handling, and deploy runtime monitoring to detect anomalous query patterns (e.g., recursive calls, unexpected data access). Log all queries for review and implement query whitelisting for high-risk operations. Third-party audits can also identify blind spots in your configuration.
Q: Are there open-source alternatives to XP5 that are more secure?
A: Yes. Protocols like Elasticsearch with strict query validation or Apache Solr with custom security plugins offer better out-of-the-box protections. However, security depends on implementation—even open-source tools can be misconfigured. Always validate input and enforce least-privilege access in any search system.
Q: What’s the most common attack vector in XP5 deployments?
A: The most prevalent risk is query injection via semantic enrichment, where attackers embed malicious directives in seemingly harmless searches. For example, a query like "show me all users with role='admin'" might trigger unintended privilege escalation if the parser doesn’t escape the single quotes. Fuzzy matching and dynamic field resolution further amplify this risk.
Q: How can enterprises mitigate risks without sacrificing performance?
A: Implement a multi-layered approach:
- Use query rewriting to normalize input before processing.
- Deploy a lightweight query sandbox for high-risk operations.
- Enforce role-based query restrictions (e.g., read-only for most users).
- Monitor query latency spikes, which often indicate malicious activity.
- Regularly audit query logs for patterns of abuse.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Filmfestivalcircuit.