How to Know DDOS Attacks Before They Cripple Your Systems
The first signs of a DDoS attack often arrive as subtle warnings: a sudden spike in server requests, latency that feels like a glitchy video buffer, or monitoring tools flashing red alerts. These are the moments when knowing DDoS isn’t just technical knowledge—it’s a survival skill. Unlike traditional cyberthreats that steal data, DDoS strikes by sheer force, overwhelming systems until they collapse under the weight of fake traffic. The difference between a brief disruption and a catastrophic outage often hinges on whether an organization can recognize the attack early enough to respond.
Most businesses assume DDoS is an issue for banks or e-commerce giants, but the reality is far more insidious. A targeted attack on a mid-sized healthcare provider can halt emergency services, while a poorly secured IoT device in a smart home network can become the unwitting foot soldier in a botnet army. The ability to know DDoS in its early stages isn’t just about mitigating damage—it’s about understanding the attacker’s playbook before they even make their move.
The stakes are higher than ever. In 2023 alone, DDoS attacks surged by 25%, with some campaigns generating traffic volumes exceeding 500 Gbps—enough to take down even the most robust infrastructures. Yet, many organizations remain blindsided, treating symptoms instead of addressing the root cause. The question isn’t if a DDoS will happen, but when—and whether you’ll be prepared to know DDoS before it cripples your operations.

The Complete Overview of DDoS Attacks
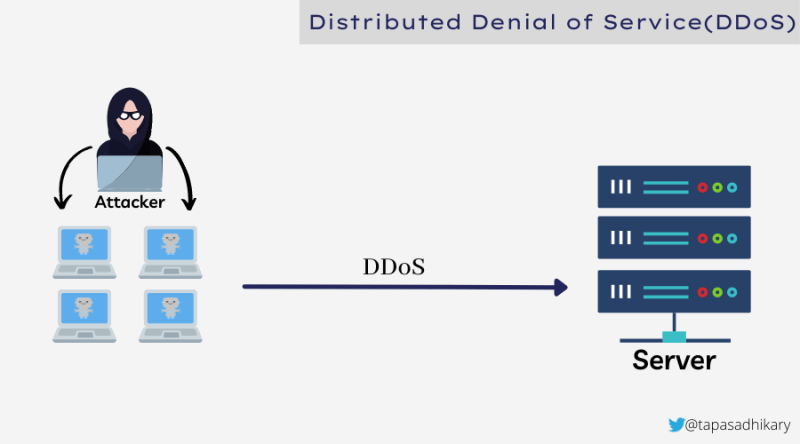
At its core, a DDoS (Distributed Denial of Service) attack is a coordinated cyber assault designed to exhaust a target’s resources—bandwidth, processing power, or memory—until legitimate users are locked out. Unlike single-source attacks, DDoS leverages botnets: networks of compromised devices (often home routers, security cameras, or infected PCs) that flood a victim with traffic from multiple vectors simultaneously. The goal isn’t theft or espionage; it’s disruption. A well-orchestrated DDoS can render a website inaccessible, paralyze cloud services, or even trigger cascading failures in critical infrastructure like power grids or financial systems.What makes DDoS uniquely dangerous is its dual nature: it’s both a tool for extortion and a smokescreen for deeper intrusions. Cybercriminals use it to distract security teams while hackers slip in to steal data or deploy ransomware. The 2021 attack on the Colonial Pipeline, which halted fuel distribution across the U.S. East Coast, began with a DDoS—followed by a ransomware payload. Understanding how to know DDoS isn’t just about stopping the flood; it’s about recognizing when the flood is a diversion for something far worse.
Historical Background and Evolution
The concept of denial-of-service (DoS) dates back to the early days of the internet, when pioneering hackers like the "Phrack crew" demonstrated how to crash systems by overwhelming them with requests. However, the modern DDoS landscape emerged in the late 1990s with the rise of botnets. The first recorded large-scale DDoS attack in 2000, against Yahoo, eBay, and Amazon, used a botnet of 80,000 infected PCs to generate 1 terabyte of traffic per second—a staggering figure at the time. Since then, the evolution has been relentless: from volumetric attacks (flooding bandwidth) to application-layer assaults (targeting specific services like APIs), and now, hybrid attacks combining multiple techniques.Today’s DDoS tactics are far more sophisticated. Attackers no longer rely solely on brute-force traffic; they exploit vulnerabilities in DNS servers, abuse memcached servers to amplify traffic by 51,000x, or even weaponize legitimate cloud services like AWS or Azure. The shift from "loud" attacks (easy to detect) to "stealthy" ones (mimicking normal traffic) has forced organizations to move beyond traditional firewalls and into behavioral analytics and AI-driven threat detection. The ability to know DDoS in 2024 requires a deeper understanding of these evolving tactics—because what worked yesterday may fail tomorrow.
Core Mechanisms: How It Works
The anatomy of a DDoS attack begins with the botnet recruitment phase, where malware infects vulnerable devices (often through unpatched software or weak credentials). These "zombies" are then controlled remotely via command-and-control (C2) servers, waiting for the attacker’s signal to launch. The actual assault unfolds in three primary layers:Table of Contents
- The Complete Overview of DDoS Attacks
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Can a DDoS attack completely shut down a website?
- Q: How do I tell if my network is under a DDoS attack?
- Q: Are home users at risk of DDoS attacks?
- Q: Can DDoS attacks be stopped completely?
- Q: What’s the difference between a DDoS and a DoS attack?
- Q: How much does DDoS protection cost?
- Q: Can DDoS attacks be used for extortion?
- Q: Are there legal consequences for launching a DDoS attack?
- Q: How can small businesses protect themselves on a budget?
- Q: What’s the most common type of DDoS attack today?
1. Volumetric Attacks: These saturate bandwidth by flooding the target with massive traffic, often using amplified protocols like DNS or NTP. A single attack can generate terabits of data, making it nearly impossible for ISPs to filter out malicious requests.
2. Protocol Attacks: These exploit weaknesses in network protocols (e.g., SYN floods, Ping of Death) to consume server resources like CPU or memory. Unlike volumetric attacks, these require less traffic but can still cripple systems.
3. Application-Layer Attacks: The most insidious type, these target specific applications (e.g., HTTP floods, slowloris attacks) by sending legitimate-looking requests that exhaust backend resources. Because they mimic normal traffic, they’re harder to detect without advanced monitoring.
The key to knowing DDoS lies in recognizing these patterns before they escalate. Traditional signature-based defenses fail here; instead, organizations must deploy anomaly detection, rate limiting, and real-time traffic analysis to distinguish between genuine users and malicious actors.
Key Benefits and Crucial Impact
The financial and operational costs of a DDoS attack extend far beyond the immediate downtime. A single hour of outage can cost a Fortune 500 company upwards of $100,000 in lost revenue, not to mention reputational damage and regulatory fines for failing to protect customer data. Yet, the most critical impact isn’t always monetary—it’s strategic. Competitors can exploit disruptions to poach customers, while attackers may use the chaos to launch secondary breaches. The ability to know DDoS before it materializes isn’t just about recovery; it’s about maintaining competitive advantage and trust.Beyond defense, understanding DDoS dynamics offers a strategic edge in cybersecurity planning. Organizations that proactively simulate attacks (via "red teaming") can identify vulnerabilities before criminals do. Insurance providers now offer DDoS-specific coverage, and cloud providers like AWS and Google Cloud have integrated anti-DDoS services into their infrastructure. The shift is clear: those who know DDoS aren’t just reacting—they’re shaping the future of digital resilience.
"A DDoS attack isn’t just a technical problem; it’s a business risk. The organizations that survive aren’t the ones with the best firewalls, but those with the foresight to treat DDoS as a strategic priority." — Mark Nunnikhoven, Former Global Lead of Threat Intelligence at Trend Micro
Major Advantages
- Early Detection: AI-driven tools can identify anomalous traffic patterns before they escalate, allowing for preemptive mitigation.
- Reduced Downtime: Automated response systems (like scrubbing centers) can filter malicious traffic in real time, minimizing service disruption.
- Cost Savings: Proactive measures (e.g., rate limiting, WAF configurations) are far cheaper than emergency response during an attack.
- Regulatory Compliance: Many industries (e.g., healthcare, finance) require DDoS preparedness as part of cybersecurity frameworks like NIST or ISO 27001.
- Competitive Edge: Organizations that know DDoS and mitigate risks faster can maintain customer trust and operational continuity during crises.
Comparative Analysis
| Traditional Firewalls | Modern DDoS Protection |
|---|---|
| Filters traffic based on predefined rules (e.g., IP blocking). | Uses behavioral analytics and machine learning to detect anomalies in real time. |
| Vulnerable to volumetric attacks (e.g., UDP floods). | Employs traffic scrubbing and rate limiting to absorb and neutralize attacks. |
| Requires manual updates to rule sets. | Automatically adapts to new attack vectors via AI-driven threat intelligence. |
| Limited visibility into application-layer attacks. | Integrates with WAFs and API gateways to monitor for slowloris or HTTP floods. |
Future Trends and Innovations
The next frontier in DDoS defense lies in predictive analytics and quantum-resistant encryption. Attackers are increasingly using AI to automate botnet recruitment and evade detection, forcing defenders to adopt similar technologies. Quantum computing could break traditional encryption methods, making DDoS attacks even more potent by enabling unprecedented traffic volumes. Meanwhile, edge computing—processing data closer to the source—is reducing latency in mitigation, allowing faster responses to localized attacks.Another emerging trend is "DDoS-as-a-Service" (DaaS), where cybercriminals rent attack capabilities from underground markets, democratizing DDoS for even non-technical attackers. This shift demands a new approach: organizations must move from reactive to proactive threat hunting, using tools like dark web monitoring to identify botnet recruitment before attacks occur. The future of knowing DDoS won’t just be about stopping the flood—it’ll be about predicting where the next one will come from.

Conclusion
The ability to know DDoS is no longer optional—it’s a necessity in an era where digital infrastructure is the backbone of global commerce. The attacks themselves are evolving, but the principles of defense remain rooted in vigilance, adaptability, and layered security. Organizations that treat DDoS as a boardroom issue—not just an IT problem—will be the ones that emerge unscathed from the next wave of cyber threats.The question isn’t whether you’ll face a DDoS; it’s whether you’ll recognize it before it’s too late. The tools exist, the strategies are proven, and the time to act is now. Knowing DDoS isn’t just about survival—it’s about leadership in an increasingly hostile digital landscape.
Comprehensive FAQs
Q: Can a DDoS attack completely shut down a website?
A: Yes. If an attack generates enough traffic (e.g., 100+ Gbps), it can exhaust a server’s bandwidth, CPU, or memory, rendering the site inaccessible to legitimate users. High-profile targets like banks or government sites often face multi-vector attacks designed to achieve this.
Q: How do I tell if my network is under a DDoS attack?
A: Key indicators include sudden traffic spikes, slow response times, increased latency, and monitoring alerts for unusual request patterns. Tools like ping, traceroute, and SIEM platforms can help identify anomalies before they escalate.
Q: Are home users at risk of DDoS attacks?
A: Indirectly. While most DDoS attacks target businesses, home devices (e.g., routers, IoT cameras) can be recruited into botnets without the owner’s knowledge. Participating in a botnet—even unknowingly—can lead to legal consequences or unintended collateral damage.
Q: Can DDoS attacks be stopped completely?
A: No, but they can be mitigated. A combination of traffic filtering, rate limiting, and scrubbing centers can neutralize most attacks. The goal isn’t perfection—it’s minimizing impact and ensuring business continuity.
Q: What’s the difference between a DDoS and a DoS attack?
A: A DoS (Denial of Service) attack uses a single source to overwhelm a target, while a DDoS (Distributed Denial of Service) attack leverages multiple compromised devices (botnets) to amplify the assault. DDoS is harder to trace and more difficult to mitigate due to its distributed nature.
Q: How much does DDoS protection cost?
A: Costs vary widely. Basic cloud-based protection (e.g., Cloudflare, Akamai) starts at ~$50/month, while enterprise-grade solutions (including on-premise scrubbing centers) can exceed $10,000/year. The investment is justified when considering the potential losses from a single attack.
Q: Can DDoS attacks be used for extortion?
A: Yes. Attackers often demand ransom payments to stop the assault, a tactic known as "DDoS-for-hire" or "ransom DDoS." Paying doesn’t guarantee the attack will stop—it only funds further criminal activity.
Q: Are there legal consequences for launching a DDoS attack?
A: Absolutely. In the U.S., the Computer Fraud and Abuse Act (CFAA) and Computer Misuse Act (UK) classify DDoS as cybercrime, punishable by fines and imprisonment. Even unintentional participation (e.g., via an infected device) can lead to legal trouble.
Q: How can small businesses protect themselves on a budget?
A: Start with free tools like fail2ban (for Linux servers) and enable rate limiting on web servers. Cloudflare’s free tier offers basic DDoS protection, and ISPs like Comcast provide anti-DDoS services for residential customers. Education (e.g., patching devices, using strong passwords) is the first line of defense.
Q: What’s the most common type of DDoS attack today?
A: Application-layer attacks (e.g., HTTP floods, slowloris) are rising rapidly because they’re harder to detect than volumetric attacks. They target specific services (e.g., APIs, login pages) with legitimate-looking traffic, making them a favorite among sophisticated attackers.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Filmfestivalcircuit.