How Tracking Apps Balance Features, Privacy, and Performance
The rise of tracking apps has reshaped how businesses monitor user behavior, from e-commerce analytics to fitness app performance metrics. Yet beneath their utility lies a tension between functionality and privacy—one that defines the modern digital experience. Users demand seamless features while demanding protection against data exploitation, forcing developers to rethink how they design tracking apps features privacy performance systems. The stakes are high: a single misstep in data handling can erode trust, while overzealous privacy controls may cripple app effectiveness.
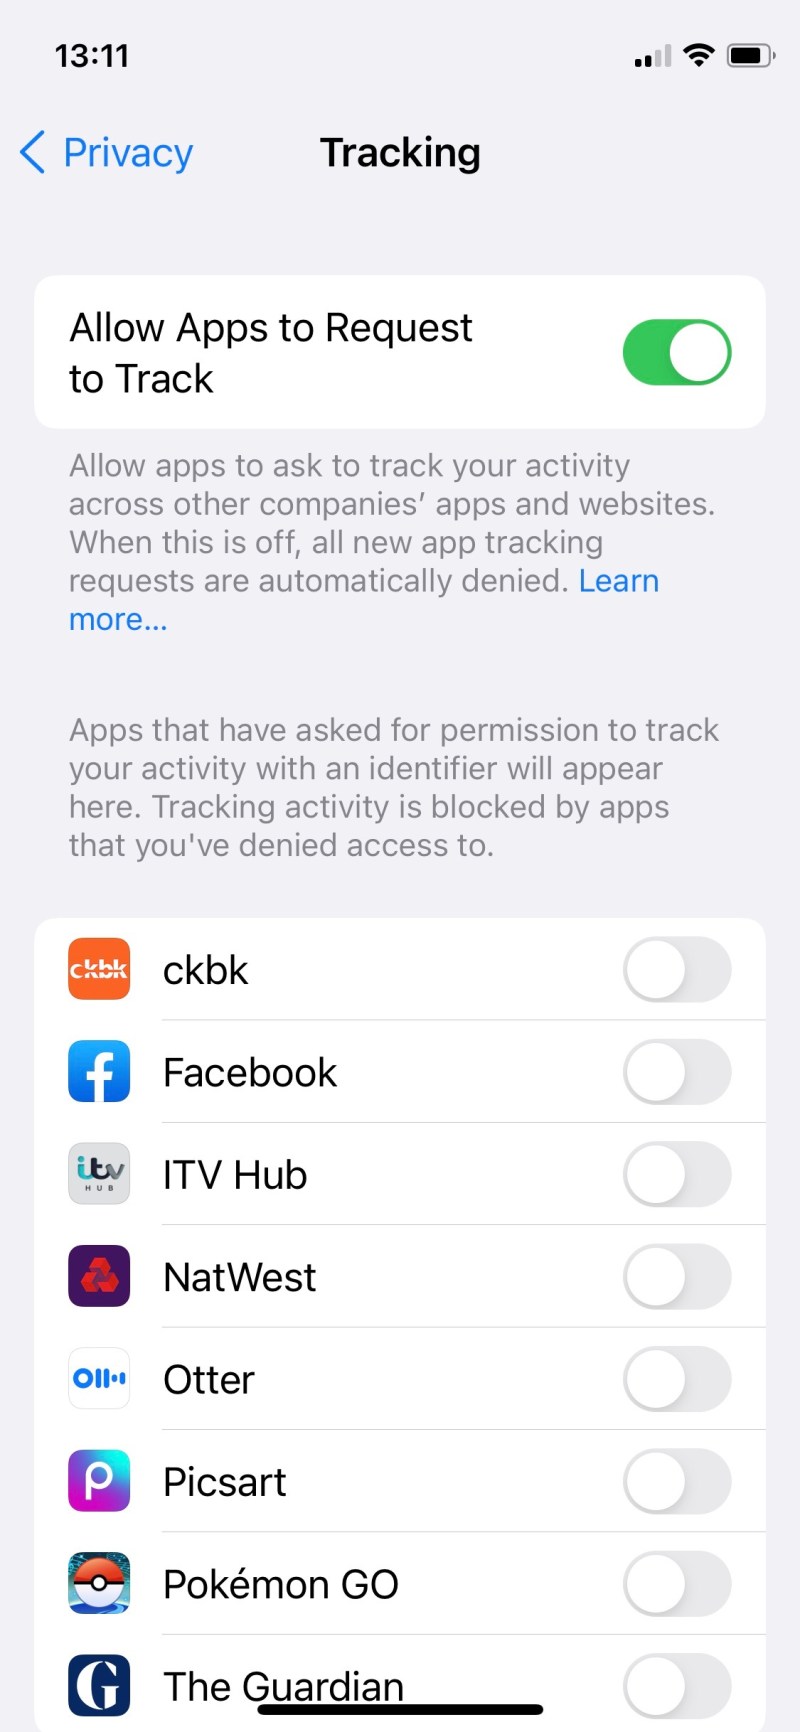
This duality isn’t theoretical. Consider the 2023 iOS privacy crackdown, which forced apps to adopt App Tracking Transparency (ATT) frameworks. Overnight, marketers saw conversion tracking accuracy plummet by 40% in some cases, while users gained granular control over their data. The conflict between tracking apps features privacy performance became impossible to ignore. Meanwhile, Android’s evolving permissions model and Europe’s GDPR enforcement have created fragmented landscapes where compliance isn’t optional—it’s a competitive differentiator.
The paradox deepens when examining real-world applications. A health app tracking steps might prioritize accuracy over anonymization, while a dating platform could bury privacy settings in labyrinthine menus to maximize data collection. The result? A fragmented ecosystem where tracking apps features privacy performance must be carefully calibrated—or risk alienating either users or stakeholders.
The Complete Overview of Tracking Apps Features Privacy Performance
At its core, the interplay between tracking apps features privacy performance represents a three-legged stool: remove one, and the system collapses. Features—such as real-time analytics, behavioral triggers, or cross-platform synchronization—drive user engagement but often rely on invasive data collection. Privacy, meanwhile, encompasses encryption, consent management, and transparency, which users increasingly demand as a baseline expectation. Performance ties them together: a laggy app with poor battery life will frustrate users regardless of its privacy stance, while overly restrictive data policies may degrade functionality to the point of uselessness.The challenge lies in designing systems where these elements coexist without compromising one another. For instance, differential privacy techniques allow apps to aggregate data without exposing individual identities, preserving both privacy and analytical utility. Similarly, edge computing reduces reliance on cloud-based tracking by processing data locally, improving performance while minimizing exposure. Yet these solutions require significant investment in infrastructure and expertise—factors that smaller developers often overlook, leading to suboptimal tracking apps features privacy performance trade-offs.
Historical Background and Evolution
The foundations of modern tracking apps were laid in the early 2000s with the advent of web analytics tools like Google Analytics, which pioneered cookie-based user behavior monitoring. These systems thrived in an era of lax privacy regulations, where tracking was treated as a necessary evil for digital growth. The shift toward mobile apps in the late 2000s intensified the debate, as smartphones became ubiquitous data collection devices. Apple’s 2012 introduction of iOS 6’s restricted background app refresh was an early warning shot, signaling that tracking apps features privacy performance would soon become a battleground.The turning point arrived in 2018 with GDPR’s implementation in the EU, which imposed strict consent requirements and data minimization principles. Suddenly, apps had to justify every piece of data they collected, forcing a reevaluation of tracking apps features privacy performance strategies. The COVID-19 pandemic accelerated this shift, as contact-tracing apps demonstrated both the power and peril of mass data collection. Meanwhile, tech giants like Meta and Google faced antitrust scrutiny, exposing how aggressive tracking fueled their dominance—while also sparking backlash from regulators and consumers alike.
Core Mechanisms: How It Works
The technical underpinnings of tracking apps features privacy performance revolve around three primary layers: data ingestion, processing, and output. Data ingestion occurs via APIs, SDKs, or direct device access (e.g., GPS, accelerometers). Apps like Strava use precise location data to map runs, while social media platforms cross-reference timestamps with ad networks to build user profiles. The trade-off here is immediate: richer data improves feature accuracy but raises privacy concerns, especially when combined with third-party sharing.Table of Contents
- The Complete Overview of Tracking Apps Features Privacy Performance
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Can tracking apps still function effectively without user consent?
- Q: How do privacy-focused tracking apps maintain performance?
- Q: What’s the biggest misconception about tracking apps and privacy?
- Q: Are there tracking apps that don’t collect personal data at all?
- Q: How can developers future-proof their tracking apps for stricter laws?
- Q: What’s the most controversial tracking feature from a privacy standpoint?
Processing is where the magic—and the ethical dilemmas—happen. Traditional methods rely on centralized servers to analyze raw data, creating single points of failure for both performance and security. Modern alternatives, such as federated learning, allow devices to process data locally before sending only aggregated insights to servers, preserving privacy without sacrificing analytical depth. Performance suffers slightly due to computational overhead, but the long-term benefits for tracking apps features privacy performance are undeniable.
Key Benefits and Crucial Impact
The demand for sophisticated tracking apps stems from their ability to transform raw user interactions into actionable insights. Businesses leverage these tools to personalize experiences, optimize ad spend, and identify growth opportunities—all of which directly impact revenue. For users, features like step counters or spending trackers deliver tangible value, reinforcing app dependency. Yet the dark side of this equation is the erosion of autonomy, as tracking often occurs without explicit awareness or meaningful control.The tension between utility and intrusion has sparked a cultural reckoning. A 2023 Pew Research study found that 68% of Americans now avoid apps with poor privacy reputations, while 42% have deleted apps over data concerns. This shift isn’t just about compliance; it’s about reputation. Brands like Duolingo and Headspace have thrived by positioning themselves as privacy-first alternatives, proving that tracking apps features privacy performance can be a competitive edge—not just a regulatory checkbox.
"Privacy isn’t a feature—it’s the foundation on which trust is built. Apps that ignore this will find themselves in the digital dustbin, no matter how flashy their tracking capabilities." — Evan Hendricks, Privacy Advocate & Author of Privacy Not Included
Major Advantages
When balanced correctly, tracking apps features privacy performance yields five key benefits:- Enhanced User Engagement: Apps that respect privacy often see higher retention rates, as users feel more secure sharing data. For example, financial apps with robust encryption attract risk-averse customers.
- Regulatory Compliance: Proactive privacy measures reduce legal risks, avoiding fines (e.g., GDPR’s €20M penalties) and reputational damage. Companies like Canva have preemptively adopted privacy-by-design principles to stay ahead of laws.
- Performance Optimization: Local data processing (e.g., on-device AI) reduces latency and bandwidth usage, improving responsiveness—critical for apps in regions with slow connectivity.
- Differentiated Market Positioning: Apps like Signal and Proton Mail leverage privacy as a selling point, attracting users disillusioned by data-hungry competitors. This "privacy premium" can justify higher pricing.
- Future-Proofing: As regulations tighten (e.g., California’s CPRA, Brazil’s LGPD), apps with scalable tracking apps features privacy performance frameworks will adapt more easily than those built on legacy tracking models.

Comparative Analysis
Not all tracking apps approach tracking apps features privacy performance equally. Below is a comparison of four major players across key dimensions:| Metric | Google Analytics (Web/Mobile) | Apple App Tracking Transparency (ATT) | Branch.io (Marketing Attribution) | OneSignal (Push Notifications) |
|---|---|---|---|---|
| Data Collection Scope | Broad (user behavior, demographics, cross-device tracking) | Limited to app-specific identifiers (IDFA) | Focused on attribution (UTM parameters, deep links) | Minimal (device tokens, opt-in push consent) |
| Privacy Controls | Opt-out via browser/device settings; GDPR/CCPA compliant | User-controlled via prompt; no tracking without consent | Granular consent management; supports privacy sandboxes | Explicit user consent for push notifications; no third-party sharing |
| Performance Impact | Moderate (SDK size ~200KB; cloud-dependent) | Minimal (lightweight prompt; no ongoing tracking) | Low (optimized SDK; edge processing available) | Negligible (lightweight SDK; local processing) |
| Compliance Readiness | Reactive (adapts to laws but often lags) | Proactive (built on privacy-by-design) | Aggressive (early adopter of privacy-preserving tech) | Moderate (focuses on notification compliance) |
Future Trends and Innovations
The next decade of tracking apps features privacy performance will be shaped by three disruptive forces: regulatory evolution, technological innovation, and user behavior shifts. On the regulatory front, the U.S. is poised to adopt a federal privacy law (modeled after GDPR or CPRA), while the EU’s Digital Services Act will impose stricter transparency requirements on tracking. Apps that fail to align with these standards risk being blacklisted by app stores or facing lawsuits.Technologically, homomorphic encryption—which allows data to be processed in encrypted form—could eliminate the need for raw data exposure, revolutionizing tracking apps features privacy performance. Similarly, decentralized identity solutions (e.g., blockchain-based credentials) may reduce reliance on third-party trackers by letting users control data access directly. Early adopters like Microsoft’s Privacy Preserving Analytics are already testing these approaches, signaling a shift toward "privacy-enhancing computation."
User expectations will also harden. Gen Z, now the largest consumer demographic, rejects traditional tracking models outright, favoring apps that offer explicit value exchange (e.g., "We’ll track your sleep if you get 10% off premium features"). This trend will push developers to adopt modular privacy designs, where tracking is opt-in by default and features degrade gracefully when data access is restricted.

Conclusion
The relationship between tracking apps features privacy performance is no longer a technical challenge—it’s a cultural one. Users are no longer passive participants in data collection; they’re active gatekeepers demanding accountability. The apps that thrive will be those that treat privacy as a feature, not an afterthought. This requires more than checkbox compliance; it demands architectural foresight, ethical design, and a willingness to sacrifice short-term convenience for long-term trust.The path forward isn’t about choosing between tracking and privacy—it’s about redefining what’s possible. Apps that embrace differential privacy, minimal viable data, and user-centric controls will not only survive regulatory scrutiny but also build loyalty in an era of heightened digital skepticism. The question isn’t whether tracking apps features privacy performance can coexist—it’s how quickly the industry will adapt to make that coexistence sustainable.
Comprehensive FAQs
Q: Can tracking apps still function effectively without user consent?
Not in most jurisdictions. Laws like GDPR and CCPA require explicit consent for tracking, while platforms like iOS and Android enforce opt-in frameworks (e.g., ATT). Even in permissive markets, apps risk reputational harm if they rely on covert tracking. The exception is aggregate, anonymized data (e.g., industry benchmarks), which often doesn’t trigger consent requirements.
Q: How do privacy-focused tracking apps maintain performance?
They use techniques like edge computing (processing data locally), data minimization (collecting only what’s necessary), and efficient algorithms (e.g., lightweight ML models). For example, a fitness app might track steps via the device’s accelerometer without uploading raw movement data, reducing latency and bandwidth use while preserving privacy.
Q: What’s the biggest misconception about tracking apps and privacy?
The myth that privacy and performance are mutually exclusive. In reality, poor performance often stems from inefficient tracking (e.g., excessive SDKs, unnecessary data syncs) rather than privacy measures. Apps that optimize for both—like using federated learning or on-device analytics—can achieve high accuracy without sacrificing speed or security.
Q: Are there tracking apps that don’t collect personal data at all?
Few, but some come close. Non-personalized analytics tools (e.g., server-side logs for website traffic) avoid user identifiers entirely. Apps like Firefox Focus or Standard Notes take this further by design, rejecting all tracking by default. However, these often trade features for privacy—for example, a fully anonymous fitness tracker might lack social sharing or personalized coaching.
Q: How can developers future-proof their tracking apps for stricter laws?
1. Adopt privacy-by-design: Integrate consent flows and data minimization from the start.
2. Use modular architectures: Separate core functionality from tracking dependencies.
3. Leverage open standards: Tools like Privacy Sandbox (Google) or Apple’s App Privacy Nutrition Labels simplify compliance.
4. Monitor regulatory sandboxes: Participate in preemptive testing (e.g., IAB’s Transparency & Consent Framework).
5. Educate users: Clear, jargon-free explanations of data use build trust and reduce pushback.
Q: What’s the most controversial tracking feature from a privacy standpoint?
Cross-app tracking—where a single entity (e.g., Meta, Google) stitches together data from multiple apps or websites to build comprehensive user profiles. This practice enables hyper-personalized ads but has led to scandals like Cambridge Analytica. Regulators are cracking down, with proposals like the EU’s Digital Markets Act targeting such "dark patterns" of data aggregation.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Filmfestivalcircuit.